BRIEFR · open source · the first Project Jupiter module
Answers, not another raw feed.
Self-hosted CVE intelligence for analysts. BRIEFR syncs NVD, CISA KEV, EPSS, MITRE, OTX and RSS into your own PostgreSQL, then turns them into a morning brief you can act on.
A morning in BRIEFR, scene by scene
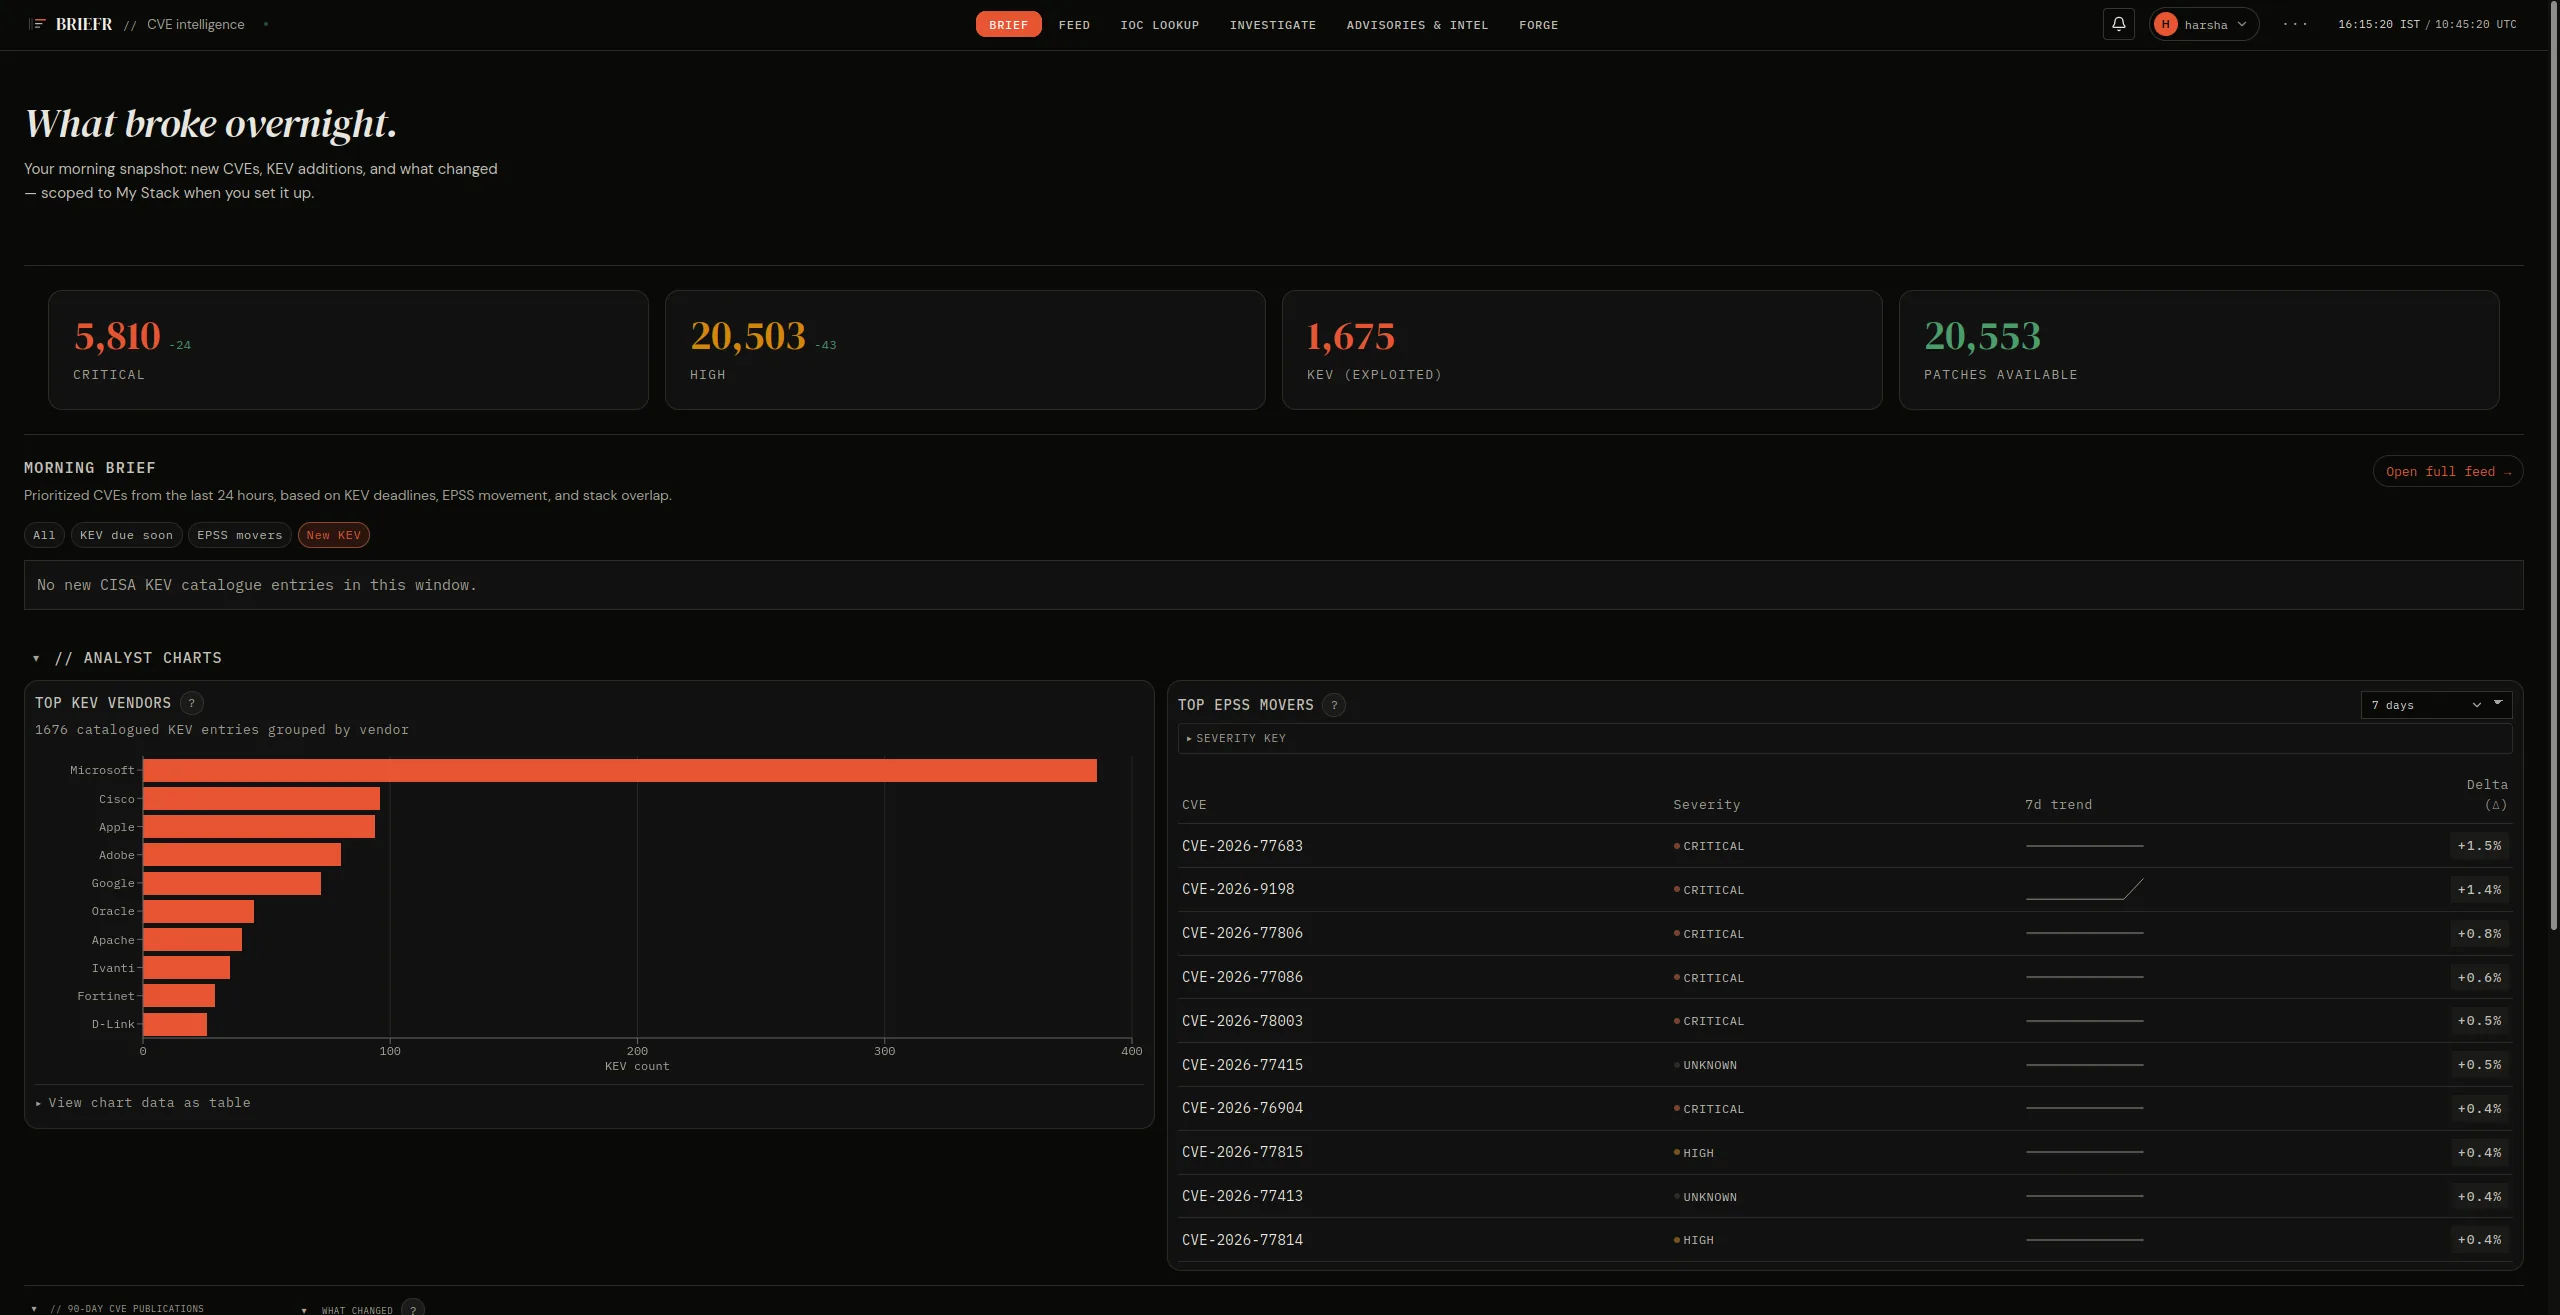
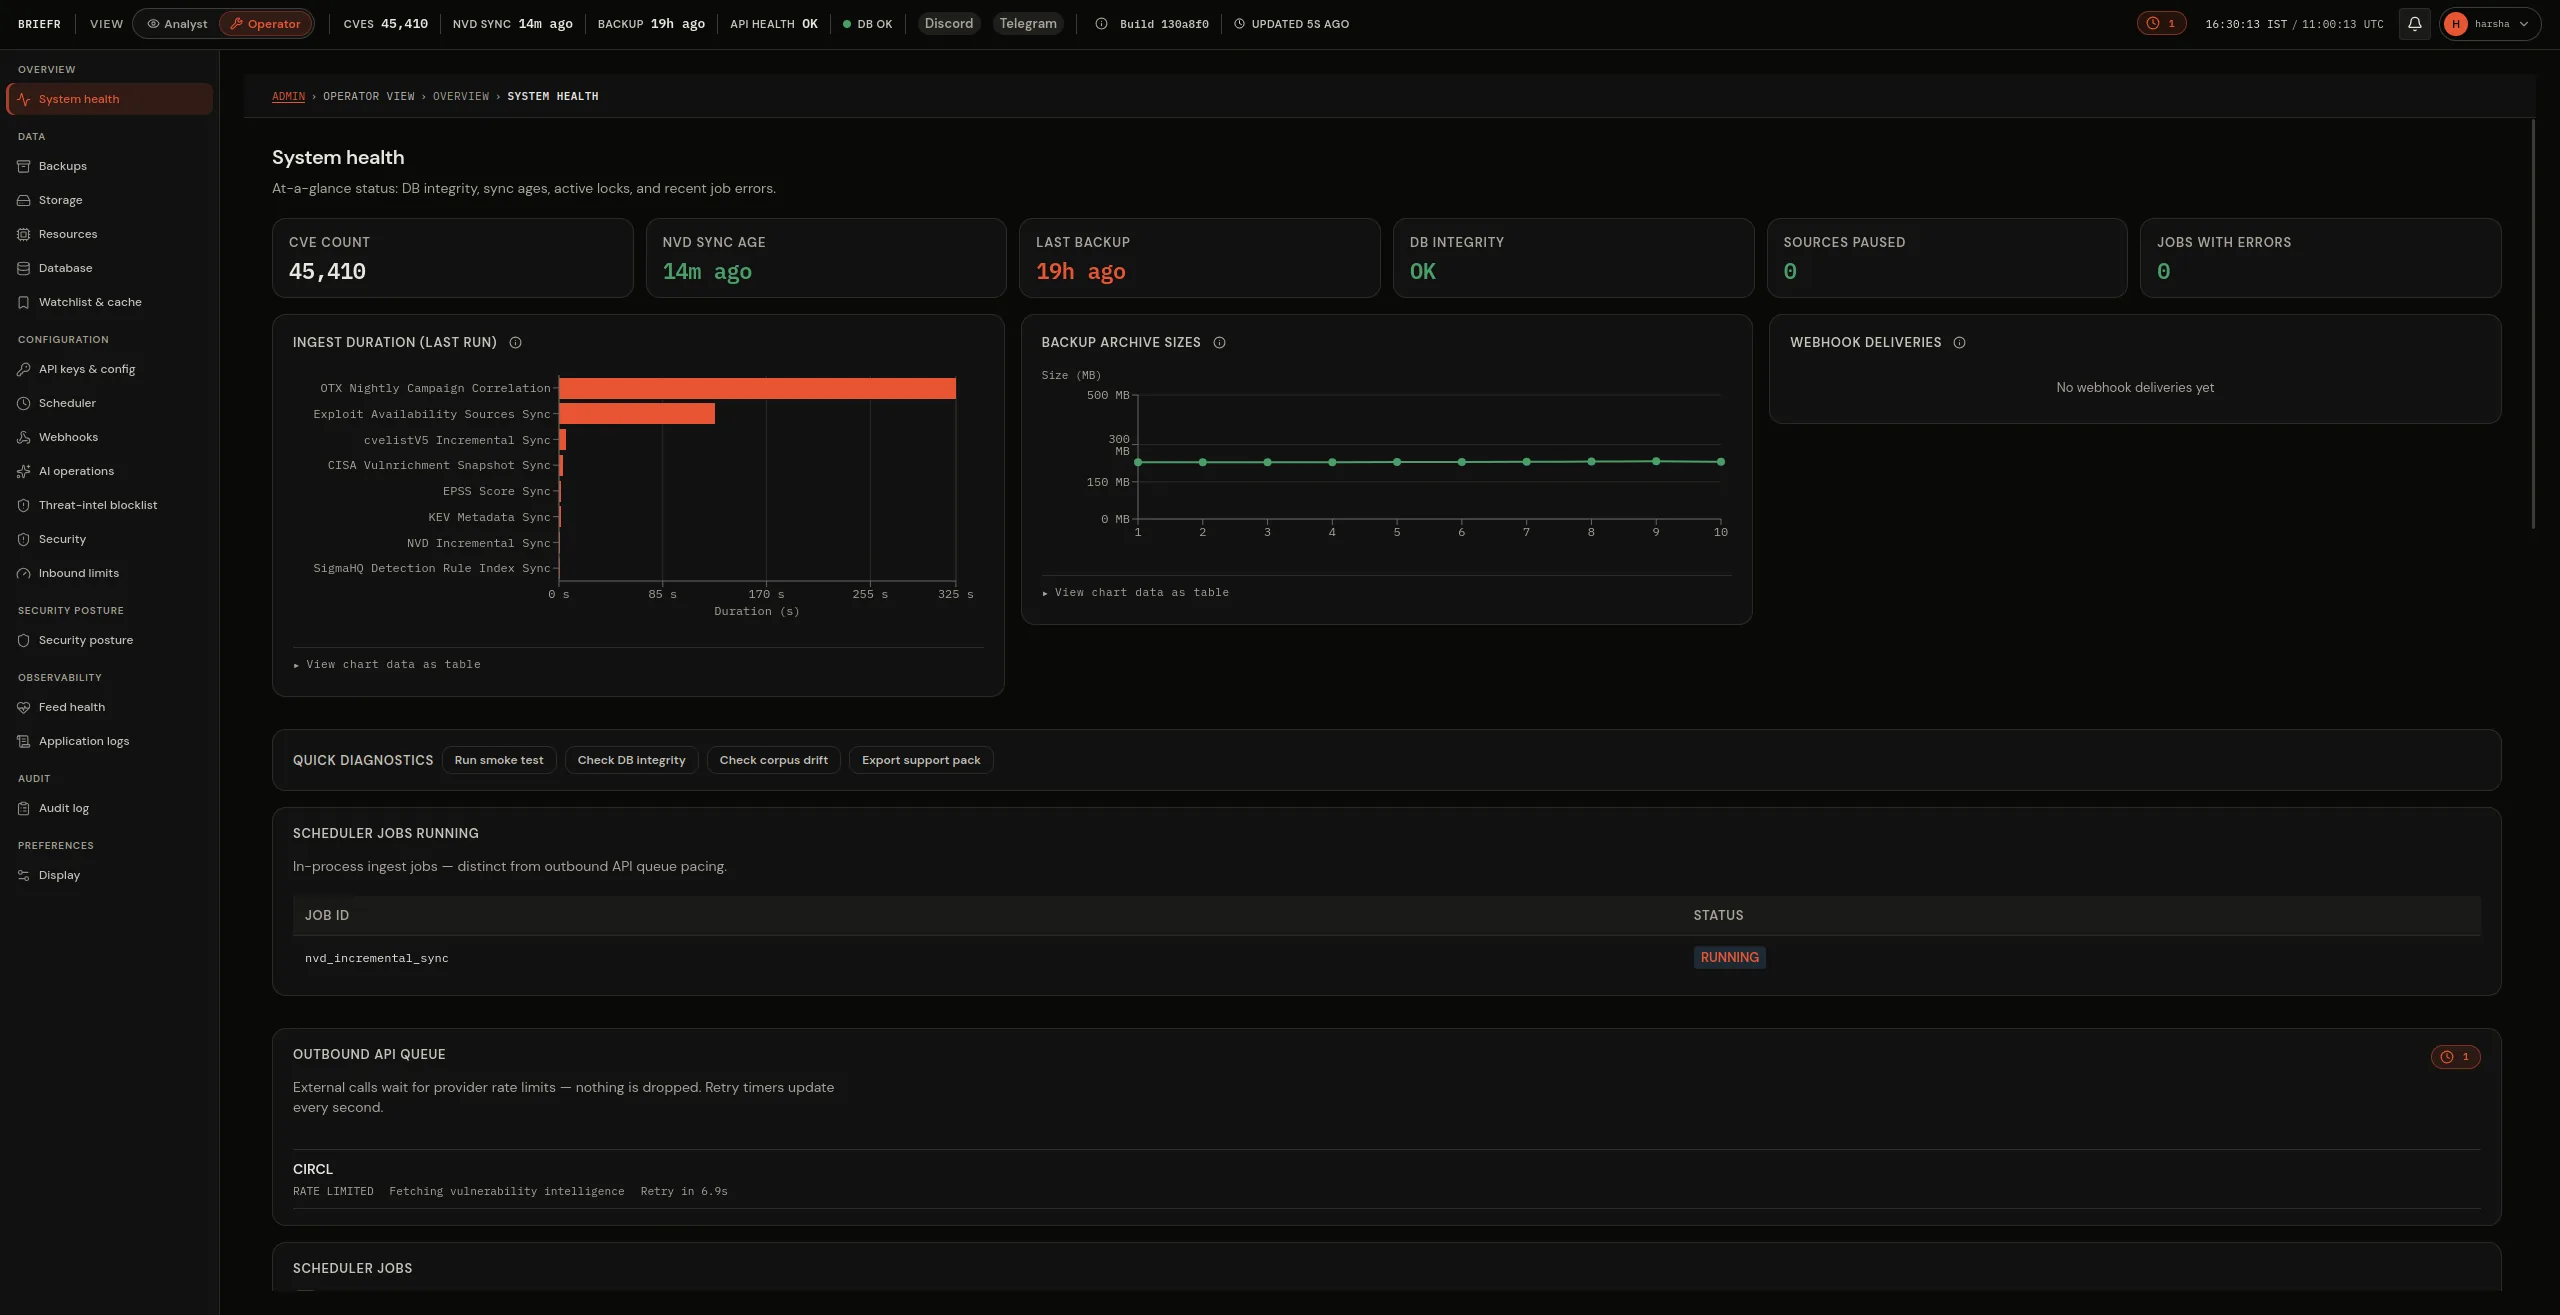
What broke overnight.
BRIEFR opens on a digest of what actually needs attention, not a raw NVD dump.
Morning brief · hero stats · what-changed deltas · 90-day heatmap
Screenshot: Briefr morning brief action queue with reason chips, hero stats, and 90-day heatmap
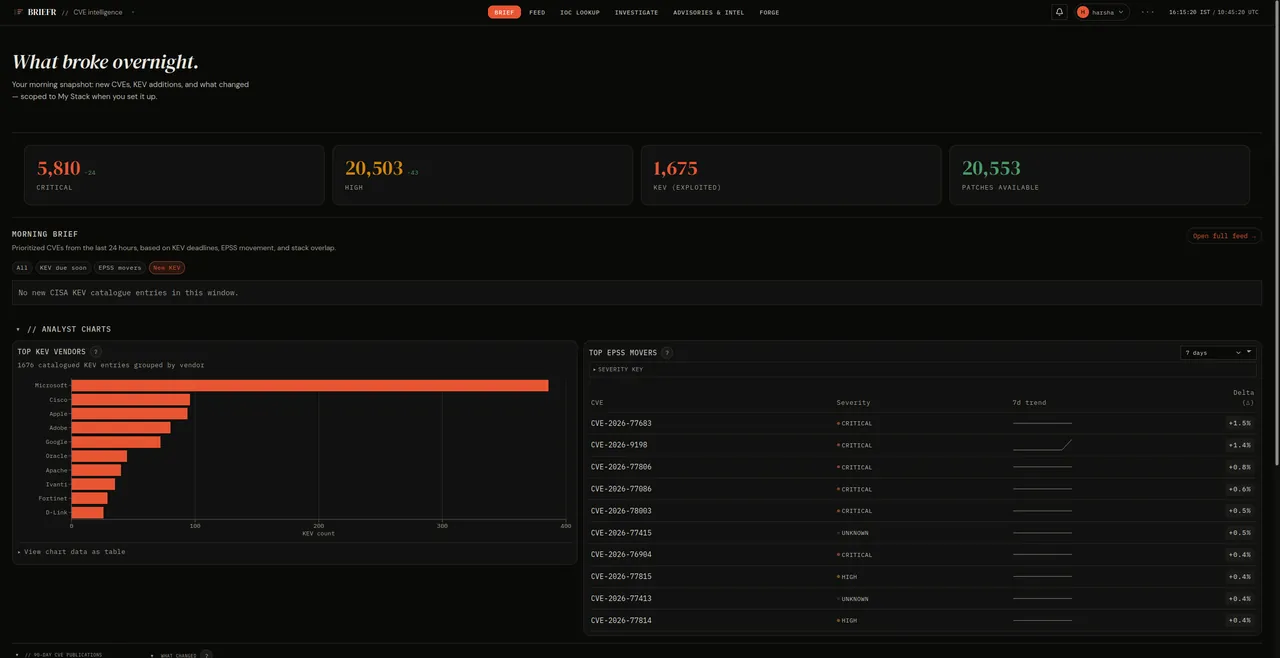
Exploited, and patchable.
Beside the severity counts: what CISA KEV lists as exploited in the wild, and what already has a patch.
Hero stats · CISA KEV · patches available
A queue with reasons attached.
Every item says why it is there: KEV due soon, an EPSS mover, a new KEV entry, or a match on your stack.
Reason chips · rule-based scoring, reproducible with zero AI keys
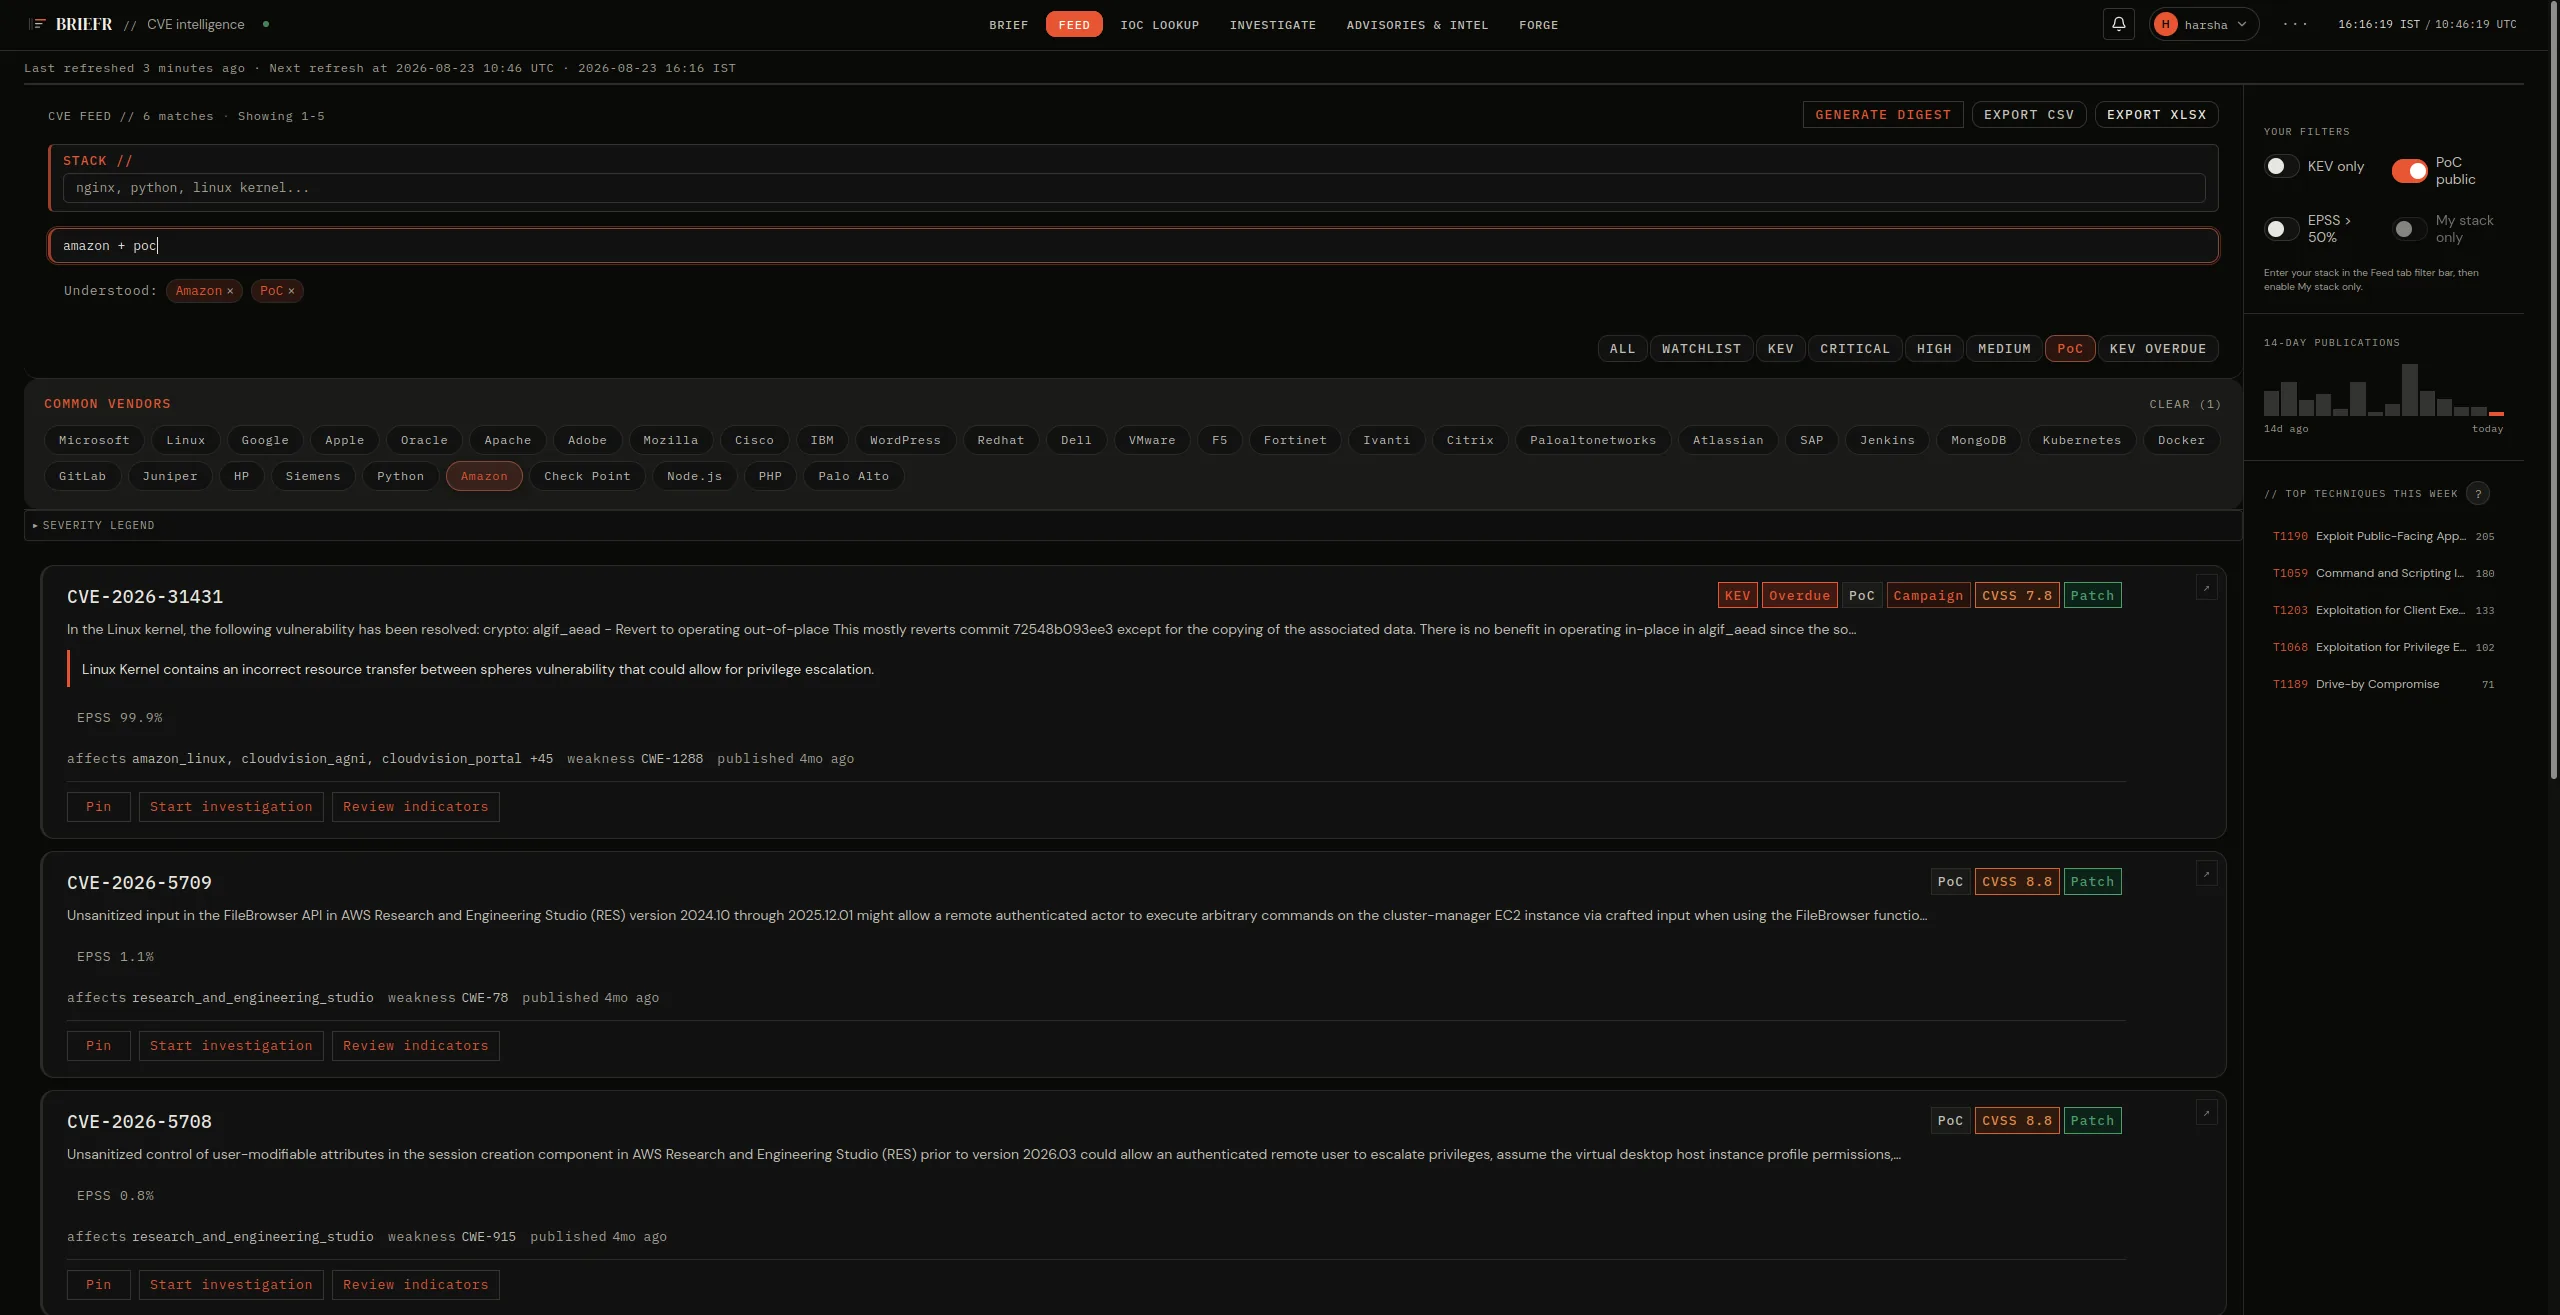
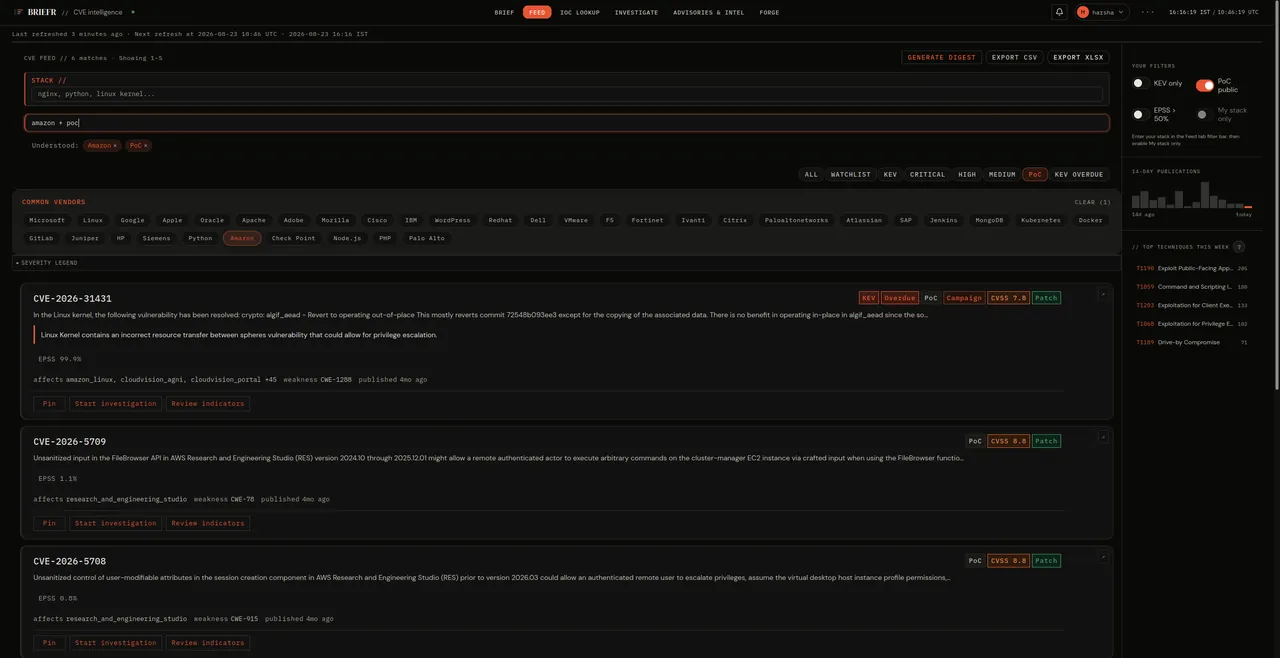
Ask the feed in plain terms.
Type “amazon + poc” and the feed reads it as a vendor and a public proof-of-concept.
Stack filter · vendor chips · KEV, EPSS and PoC filters · CSV and XLSX export
Screenshot: Briefr full CVE feed with stack filter, vendor chips, KEV sidebar, and export toolbar
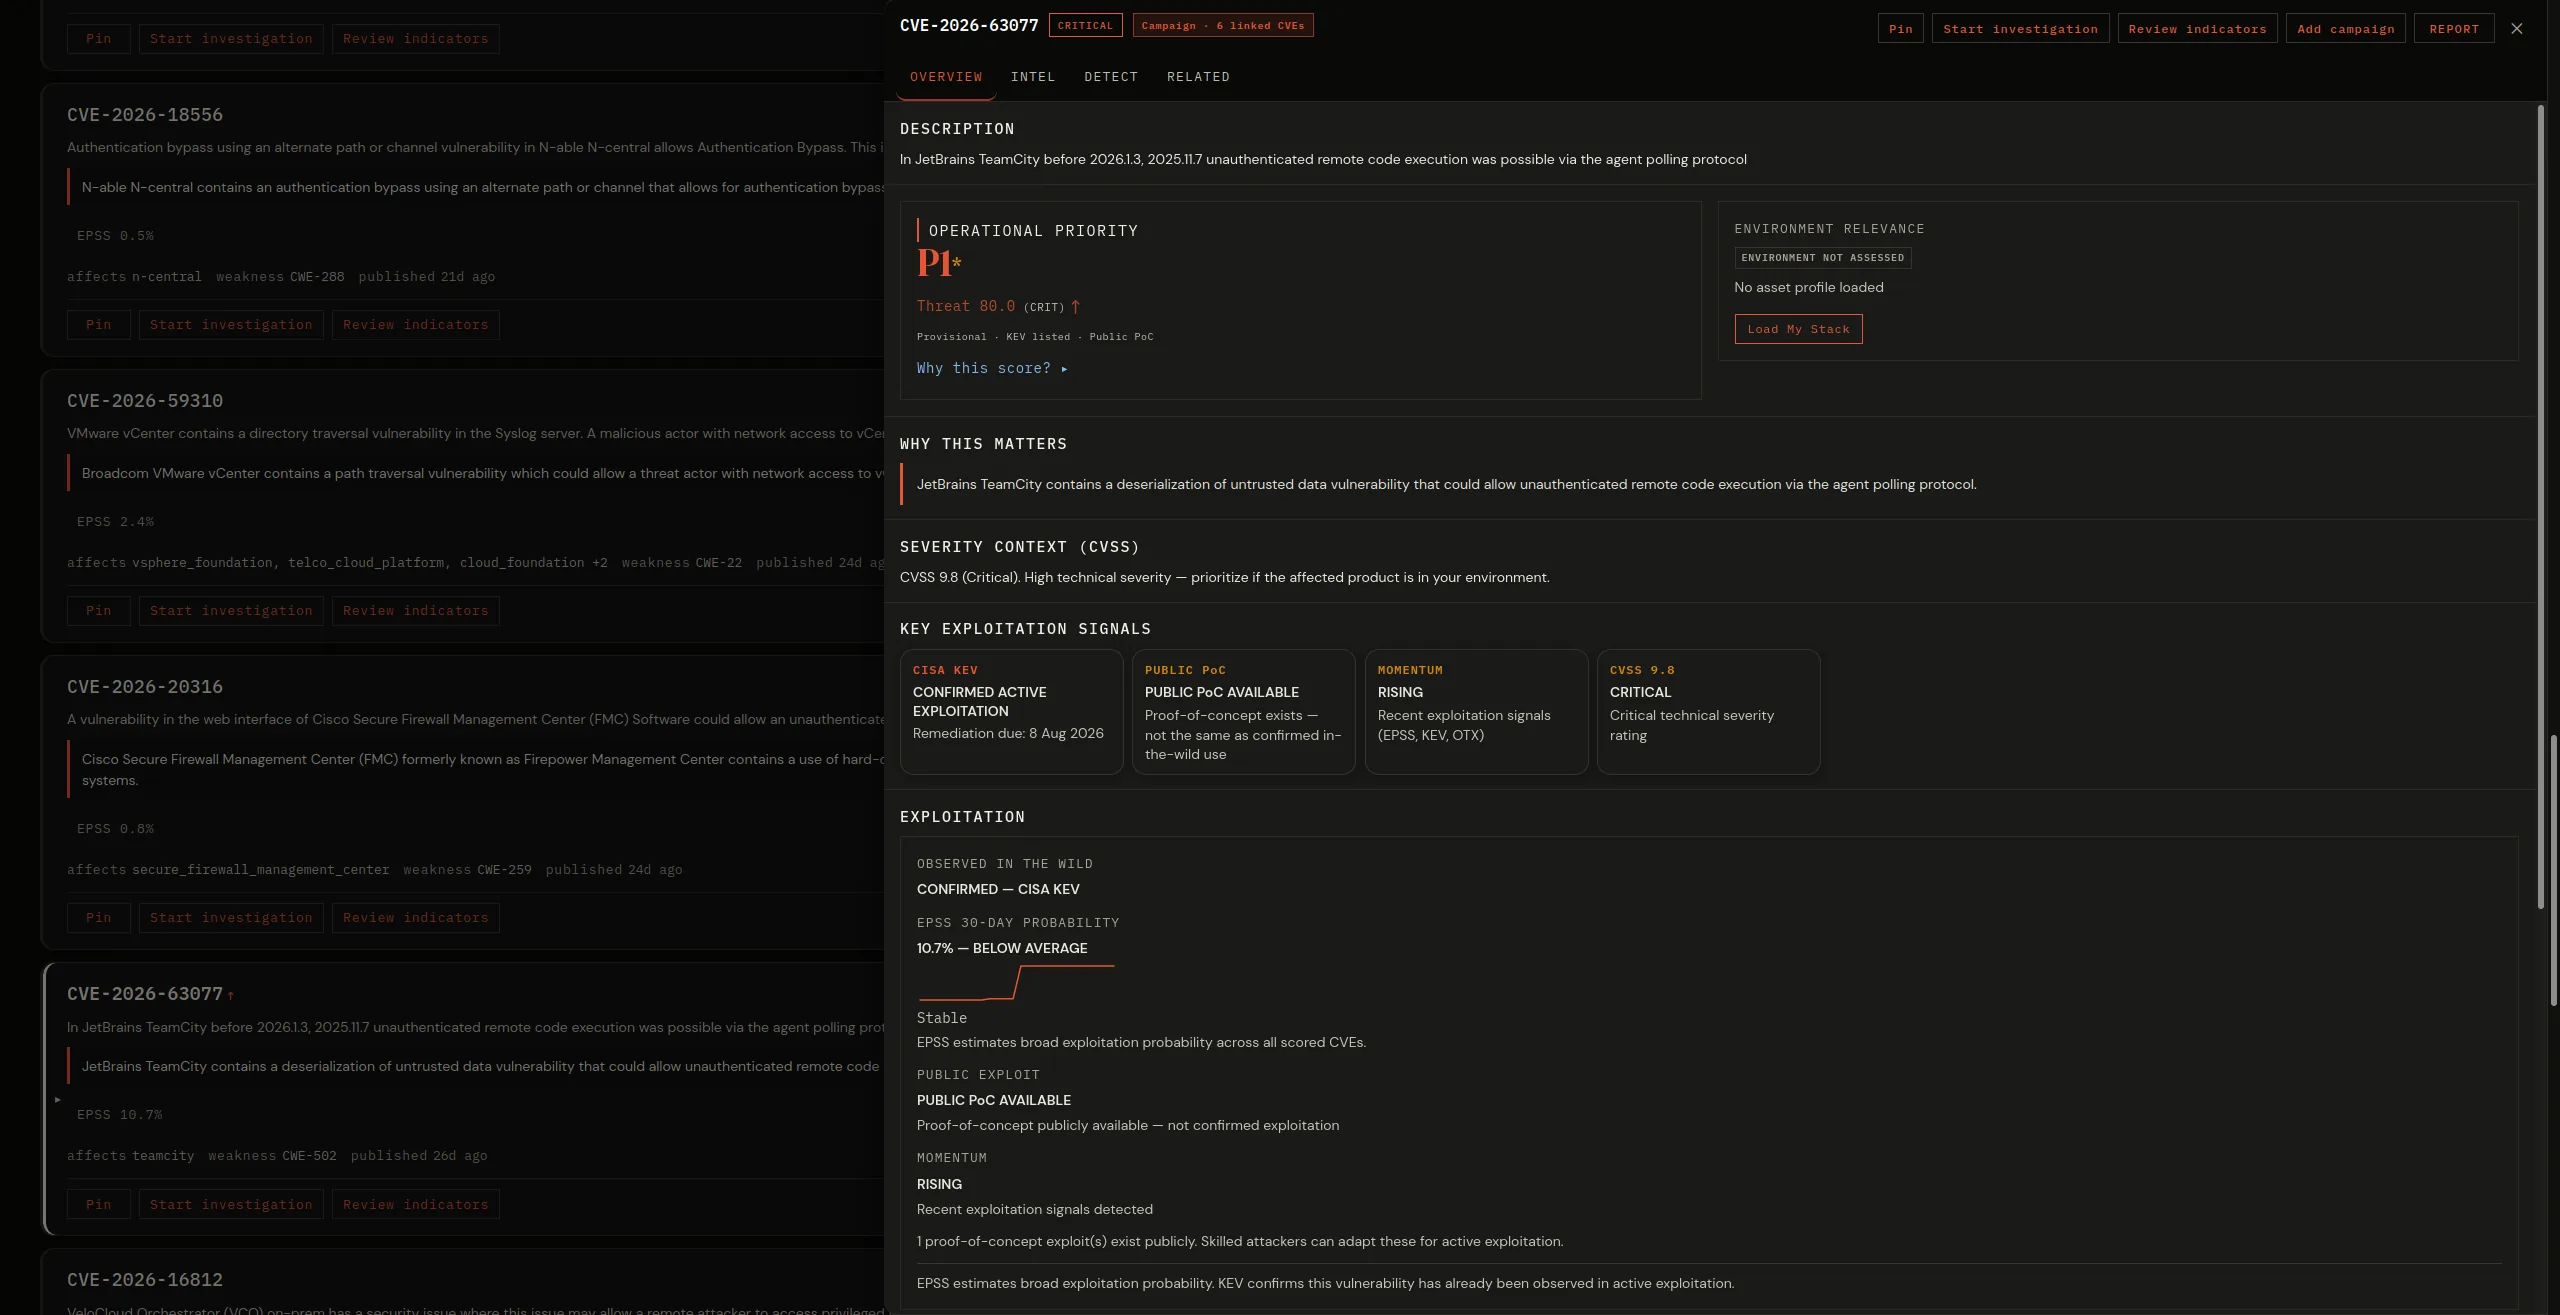
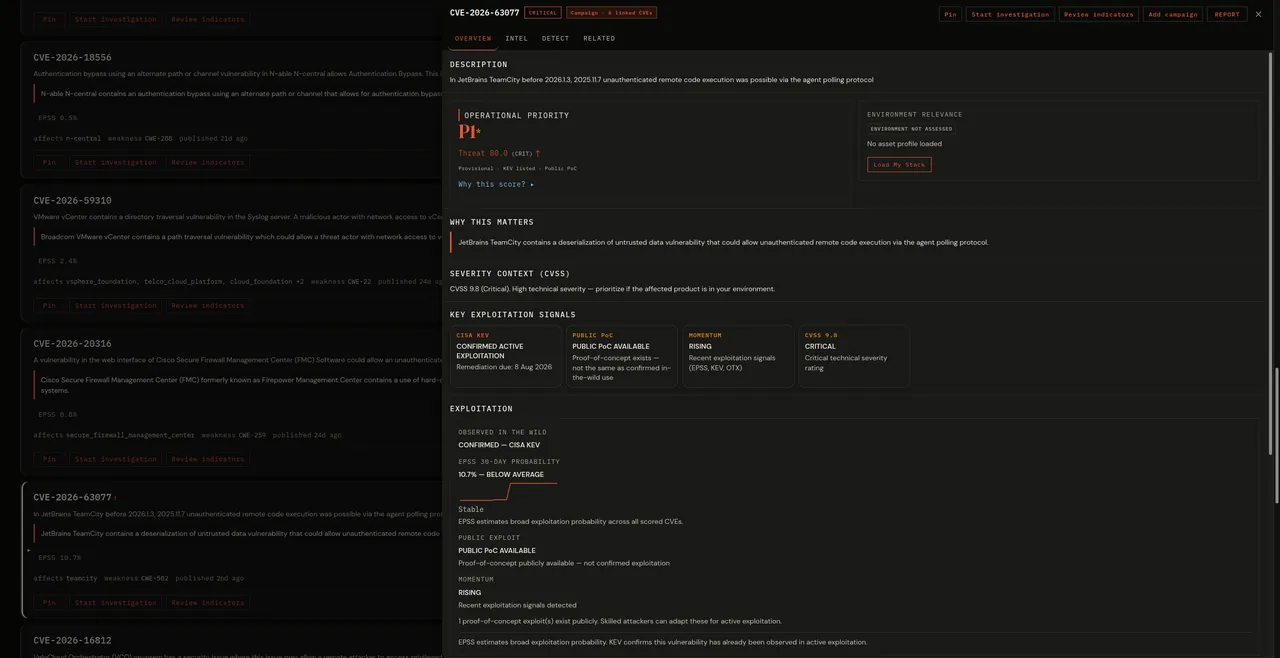
One CVE. One decision.
Operational priority comes with its reasons. Here: listed in CISA KEV, with a public PoC.
Overview · Intel · Detect · Related, without leaving the feed
Screenshot: Briefr CVE detail drawer with Intel tab, correlation, and detection context
A PoC is not exploitation.
Signals stay separate. KEV, public PoC, momentum and CVSS each say something different.
Key exploitation signals · KEV remediation due dates
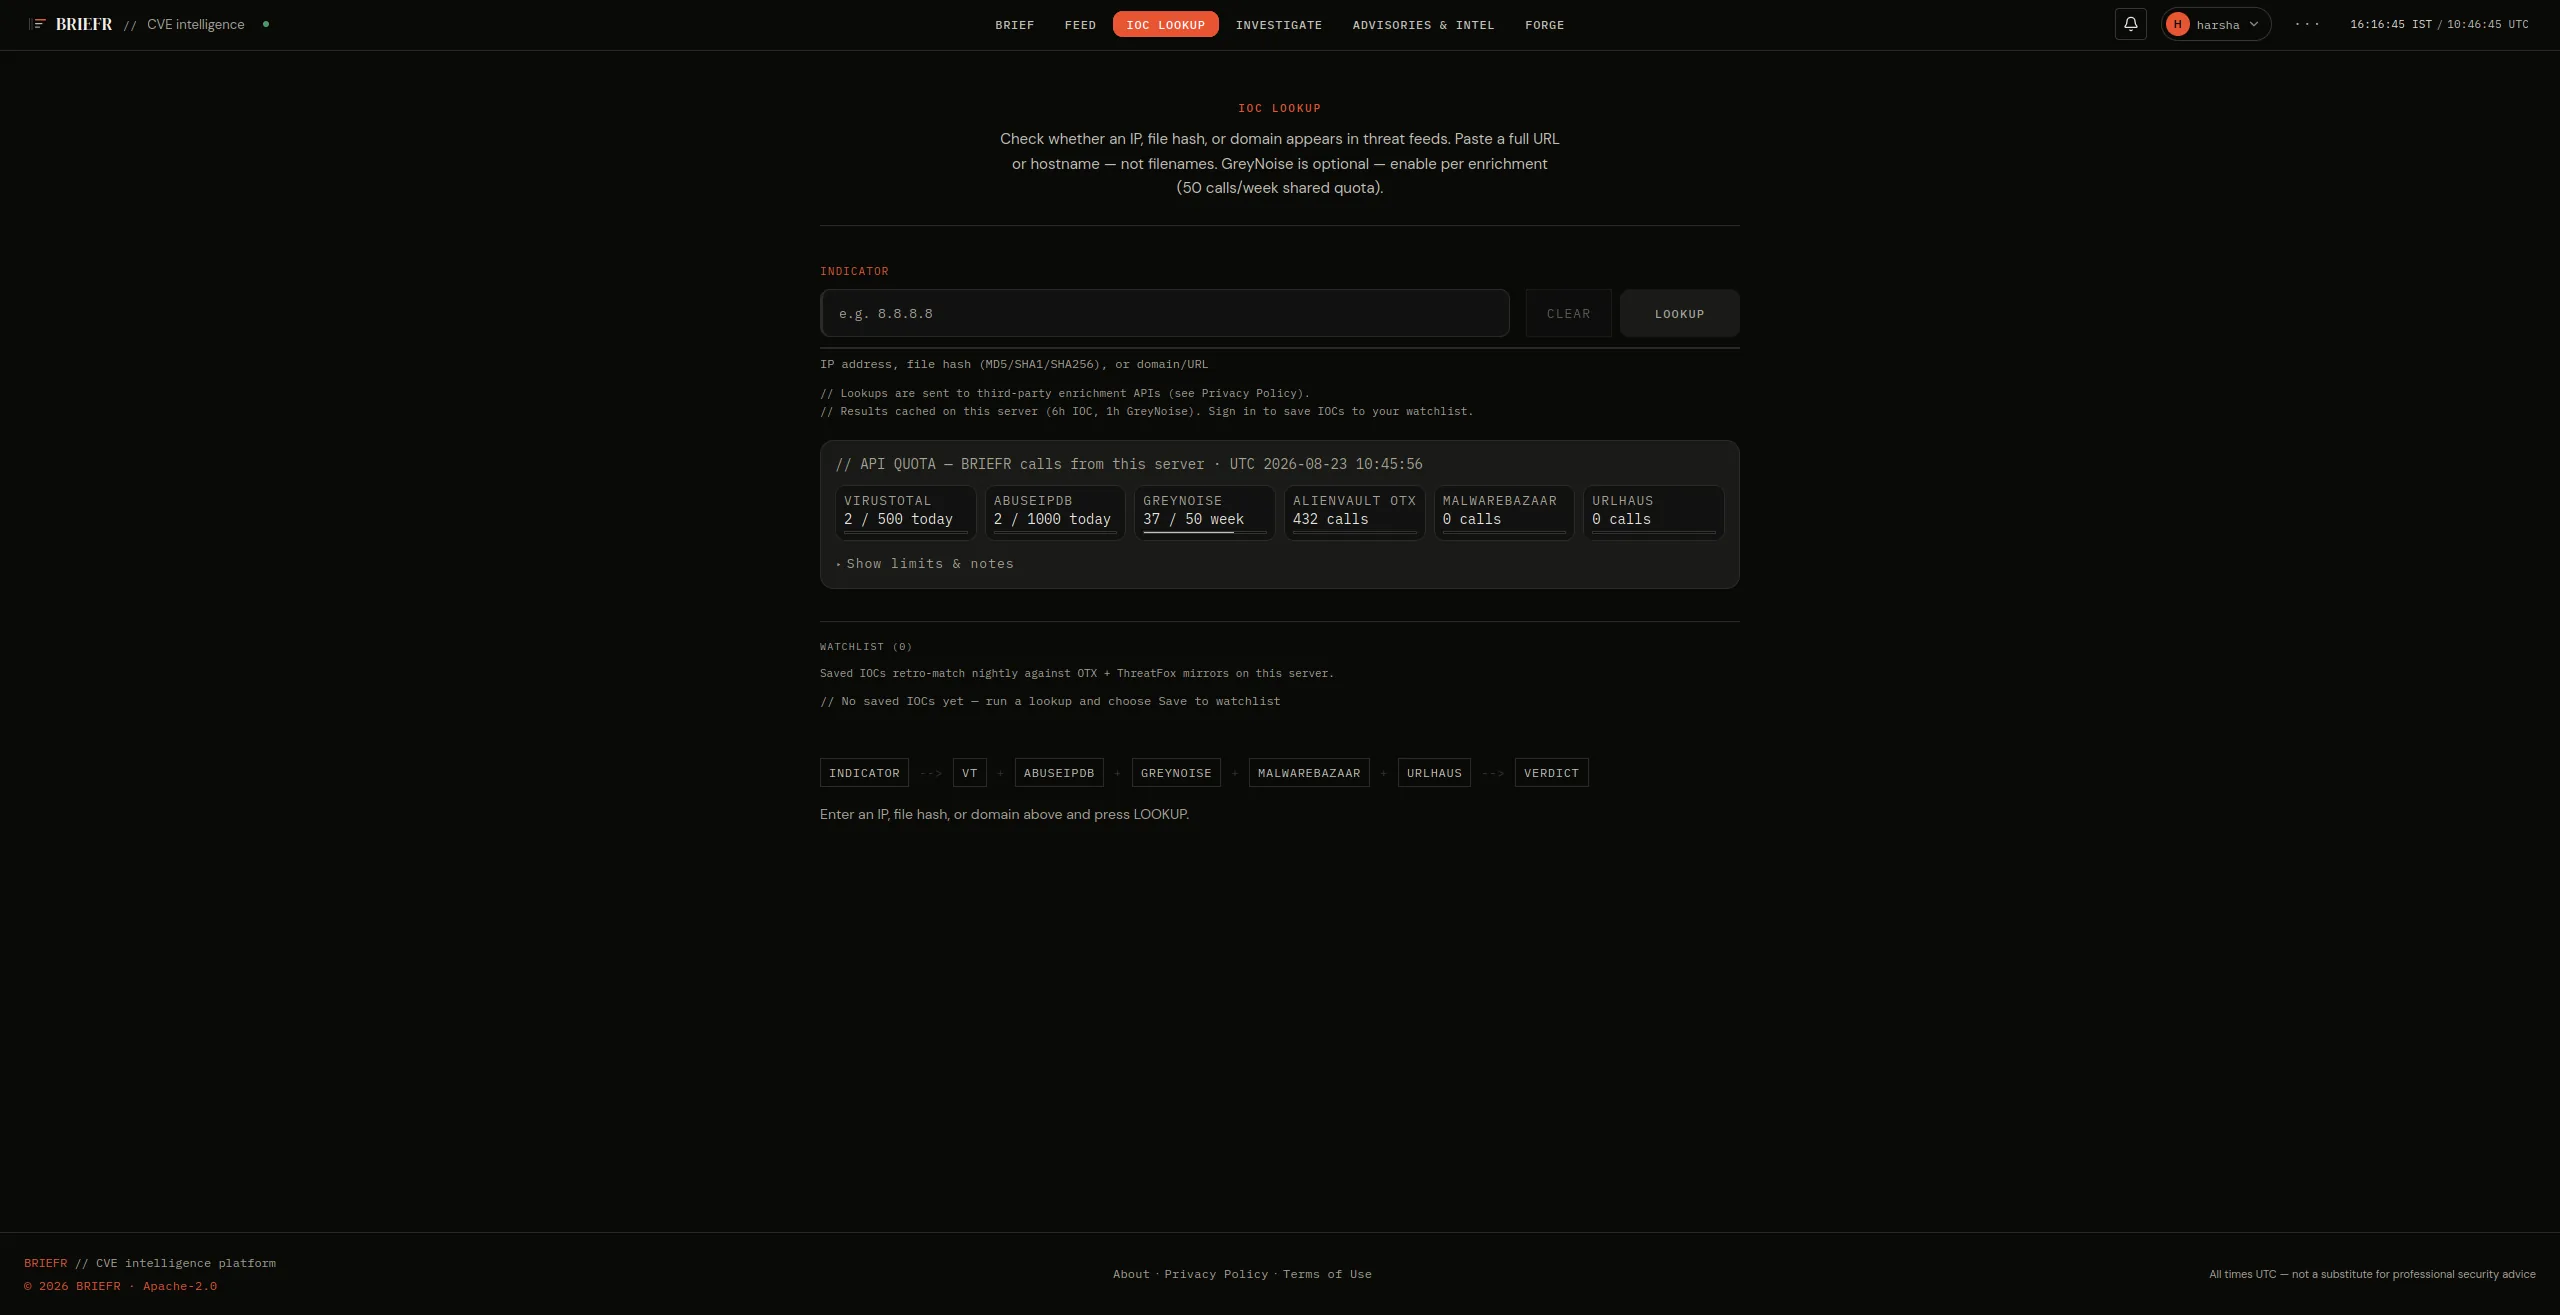
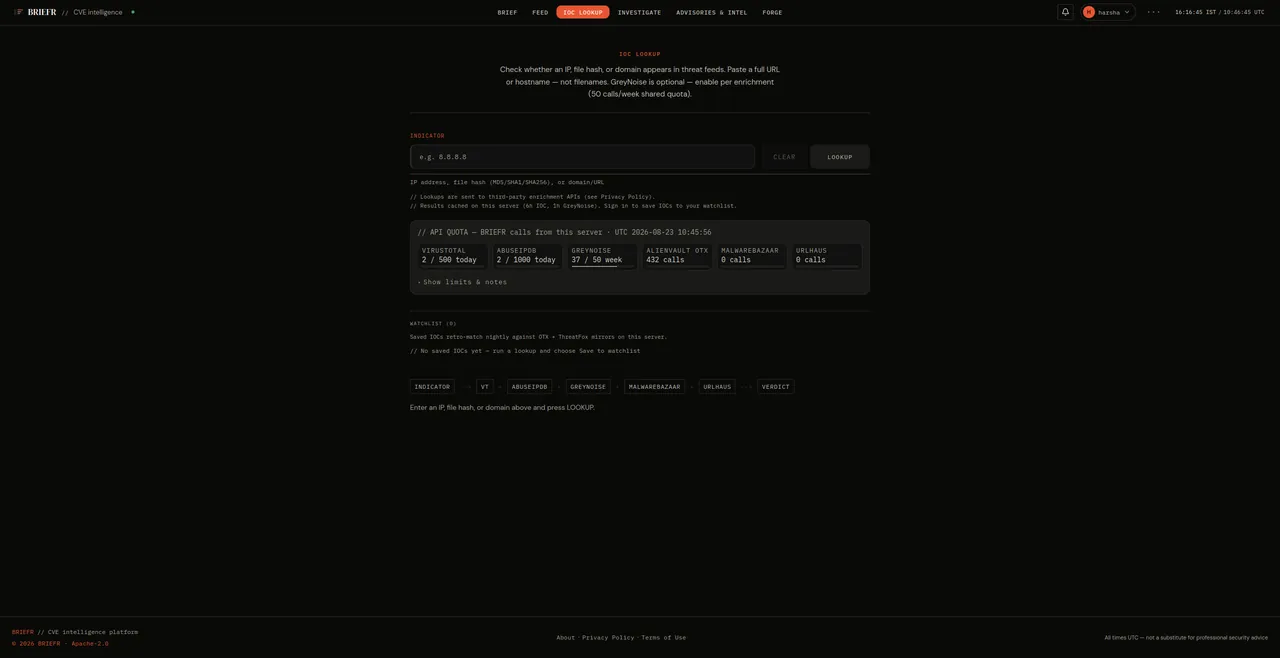
Check an indicator. Keep your quota.
IPs, hashes and domains against the sources you hold keys for, with each quota in view.
VirusTotal · AbuseIPDB · GreyNoise · OTX · MalwareBazaar · URLhaus
Screenshot: Briefr IOC lookup enriching IP, hash, and domain indicators
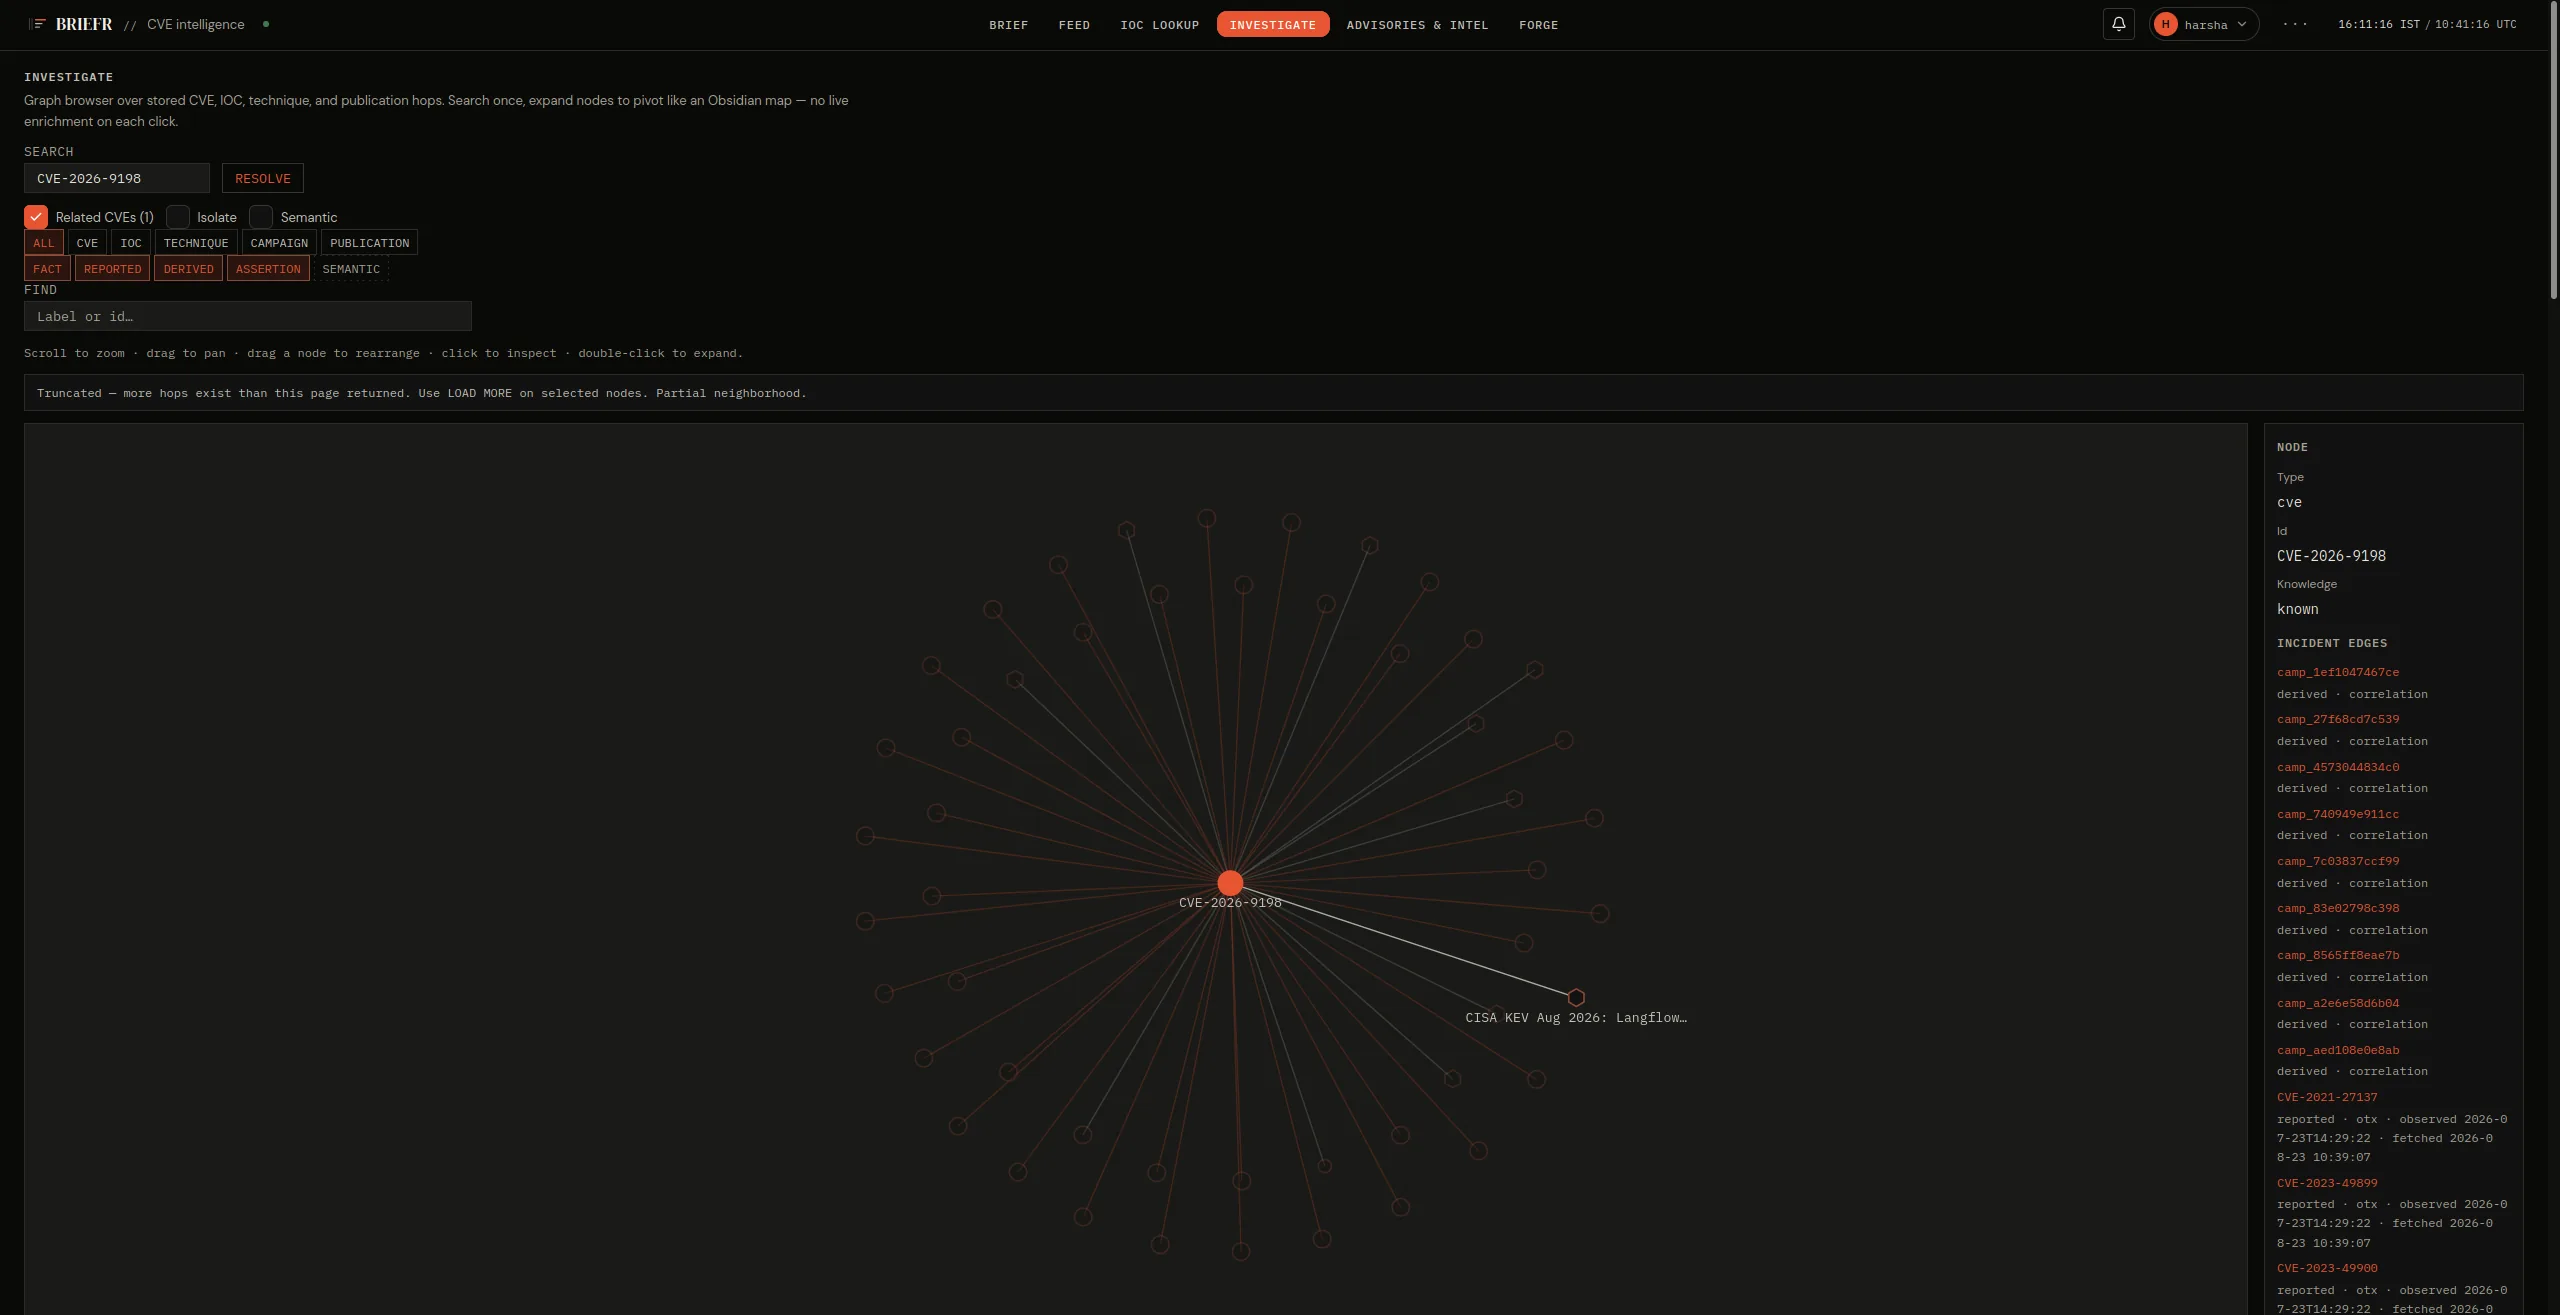
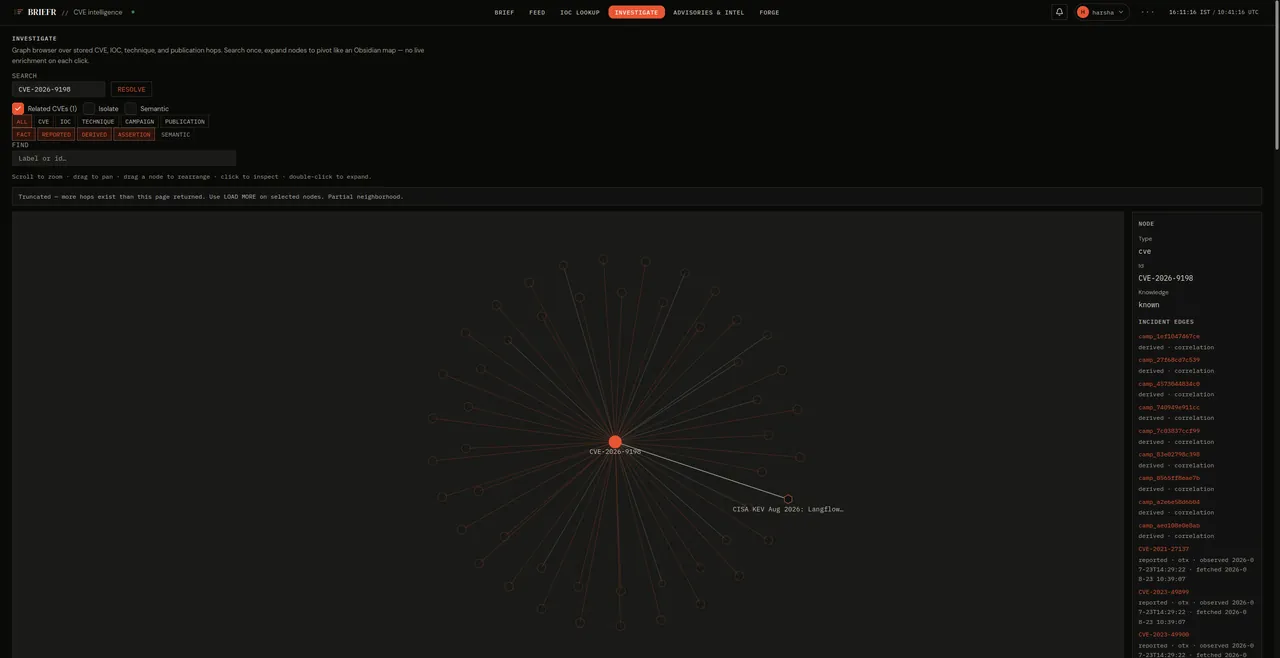
Pivot through what you already stored.
CVE, IOC, technique, campaign and publication hops, expanded from your own database.
Stored-intel graph · no live enrichment on each click
Screenshot: Briefr INVESTIGATE graph browser over stored CVE, IOC, technique, and publication hops
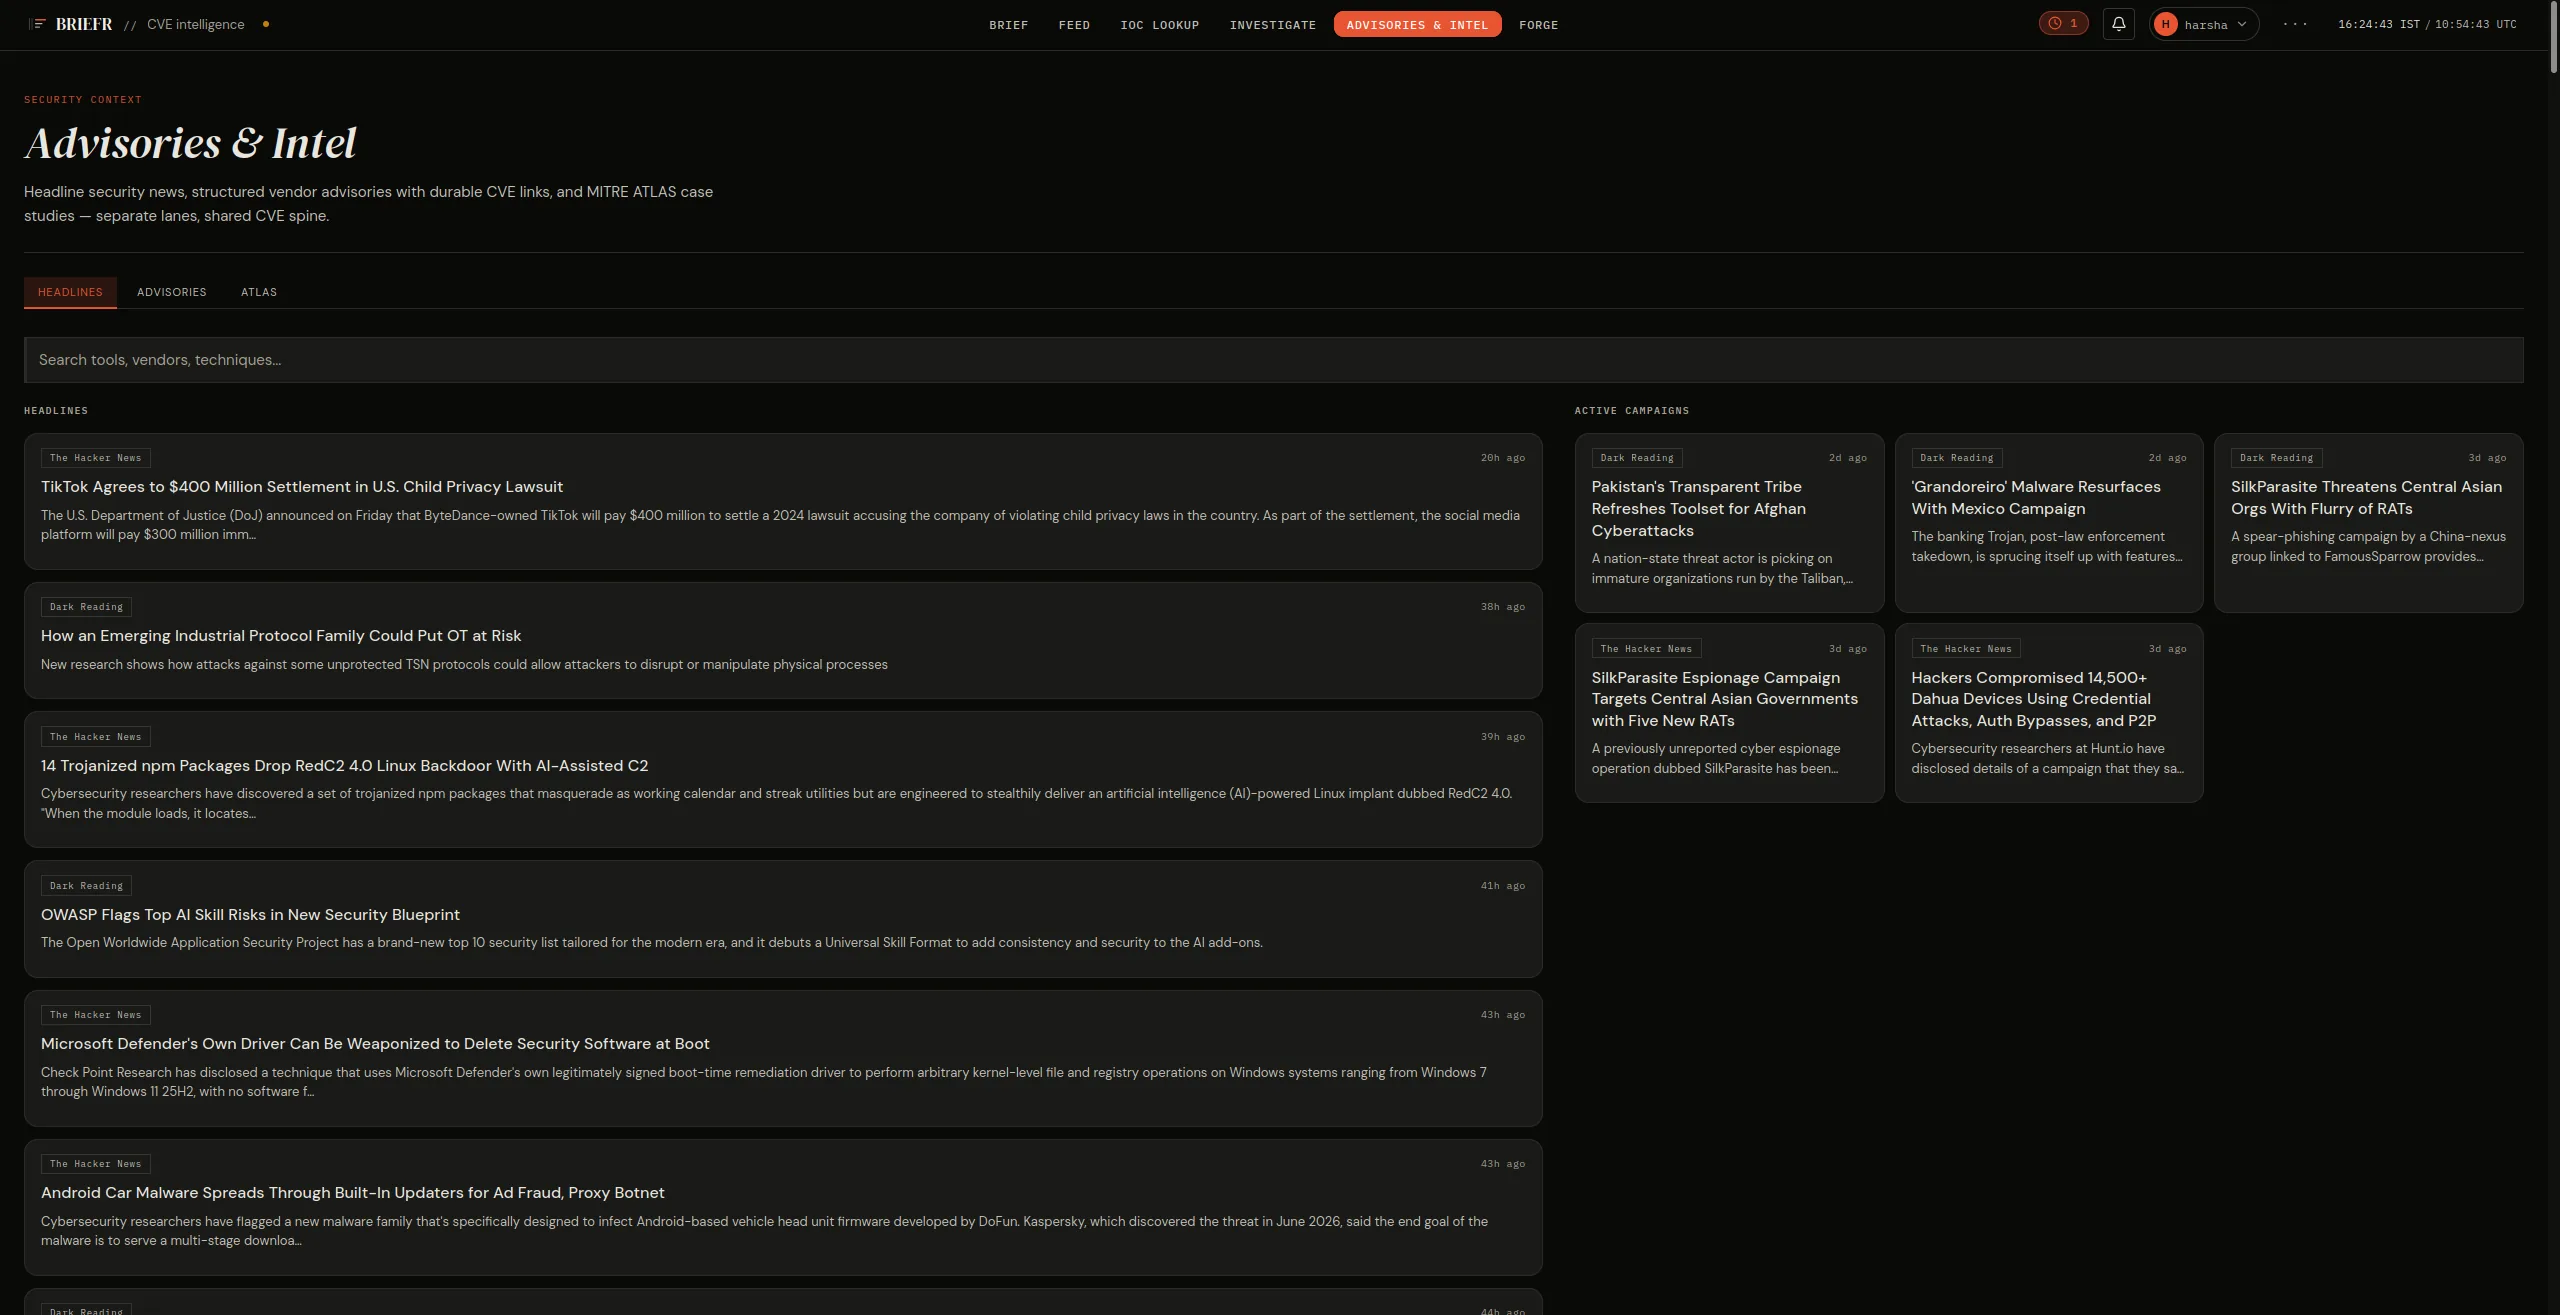
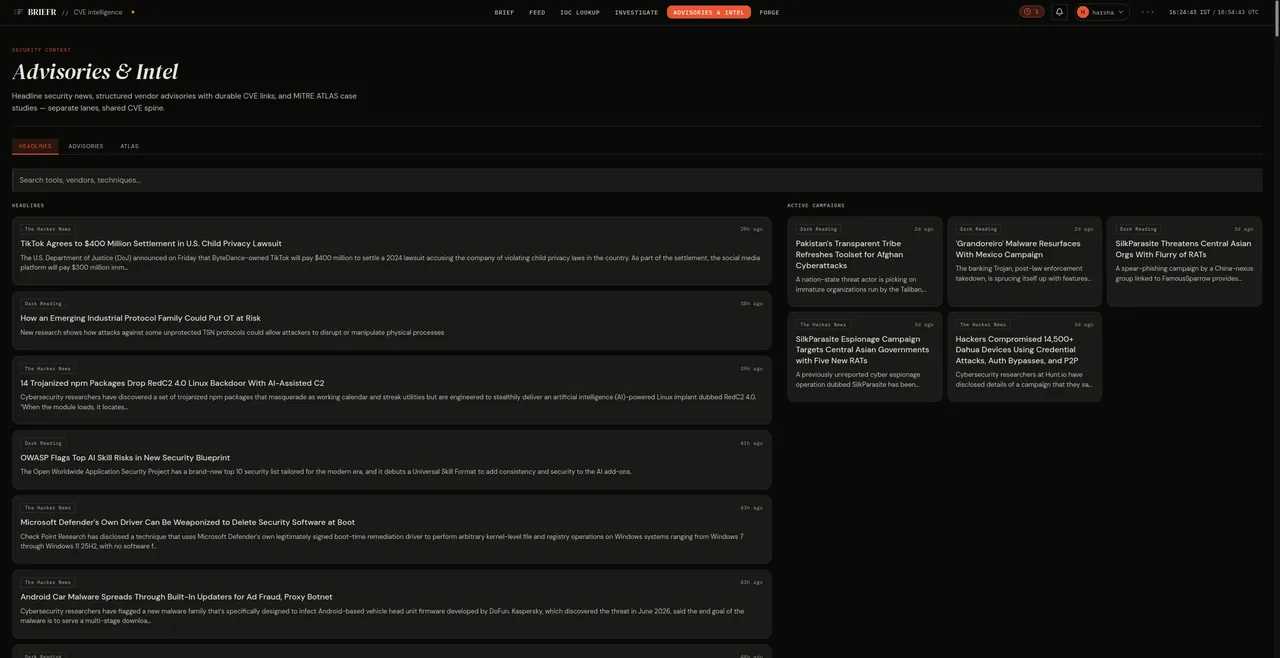
The story behind the CVE.
Headlines, structured CISA advisories and MITRE ATLAS case studies, cross-linked to CVEs.
Served from scheduler-built snapshots
Screenshot: Briefr Advisories and Intel feed with headlines, structured advisories, and MITRE ATLAS case studies
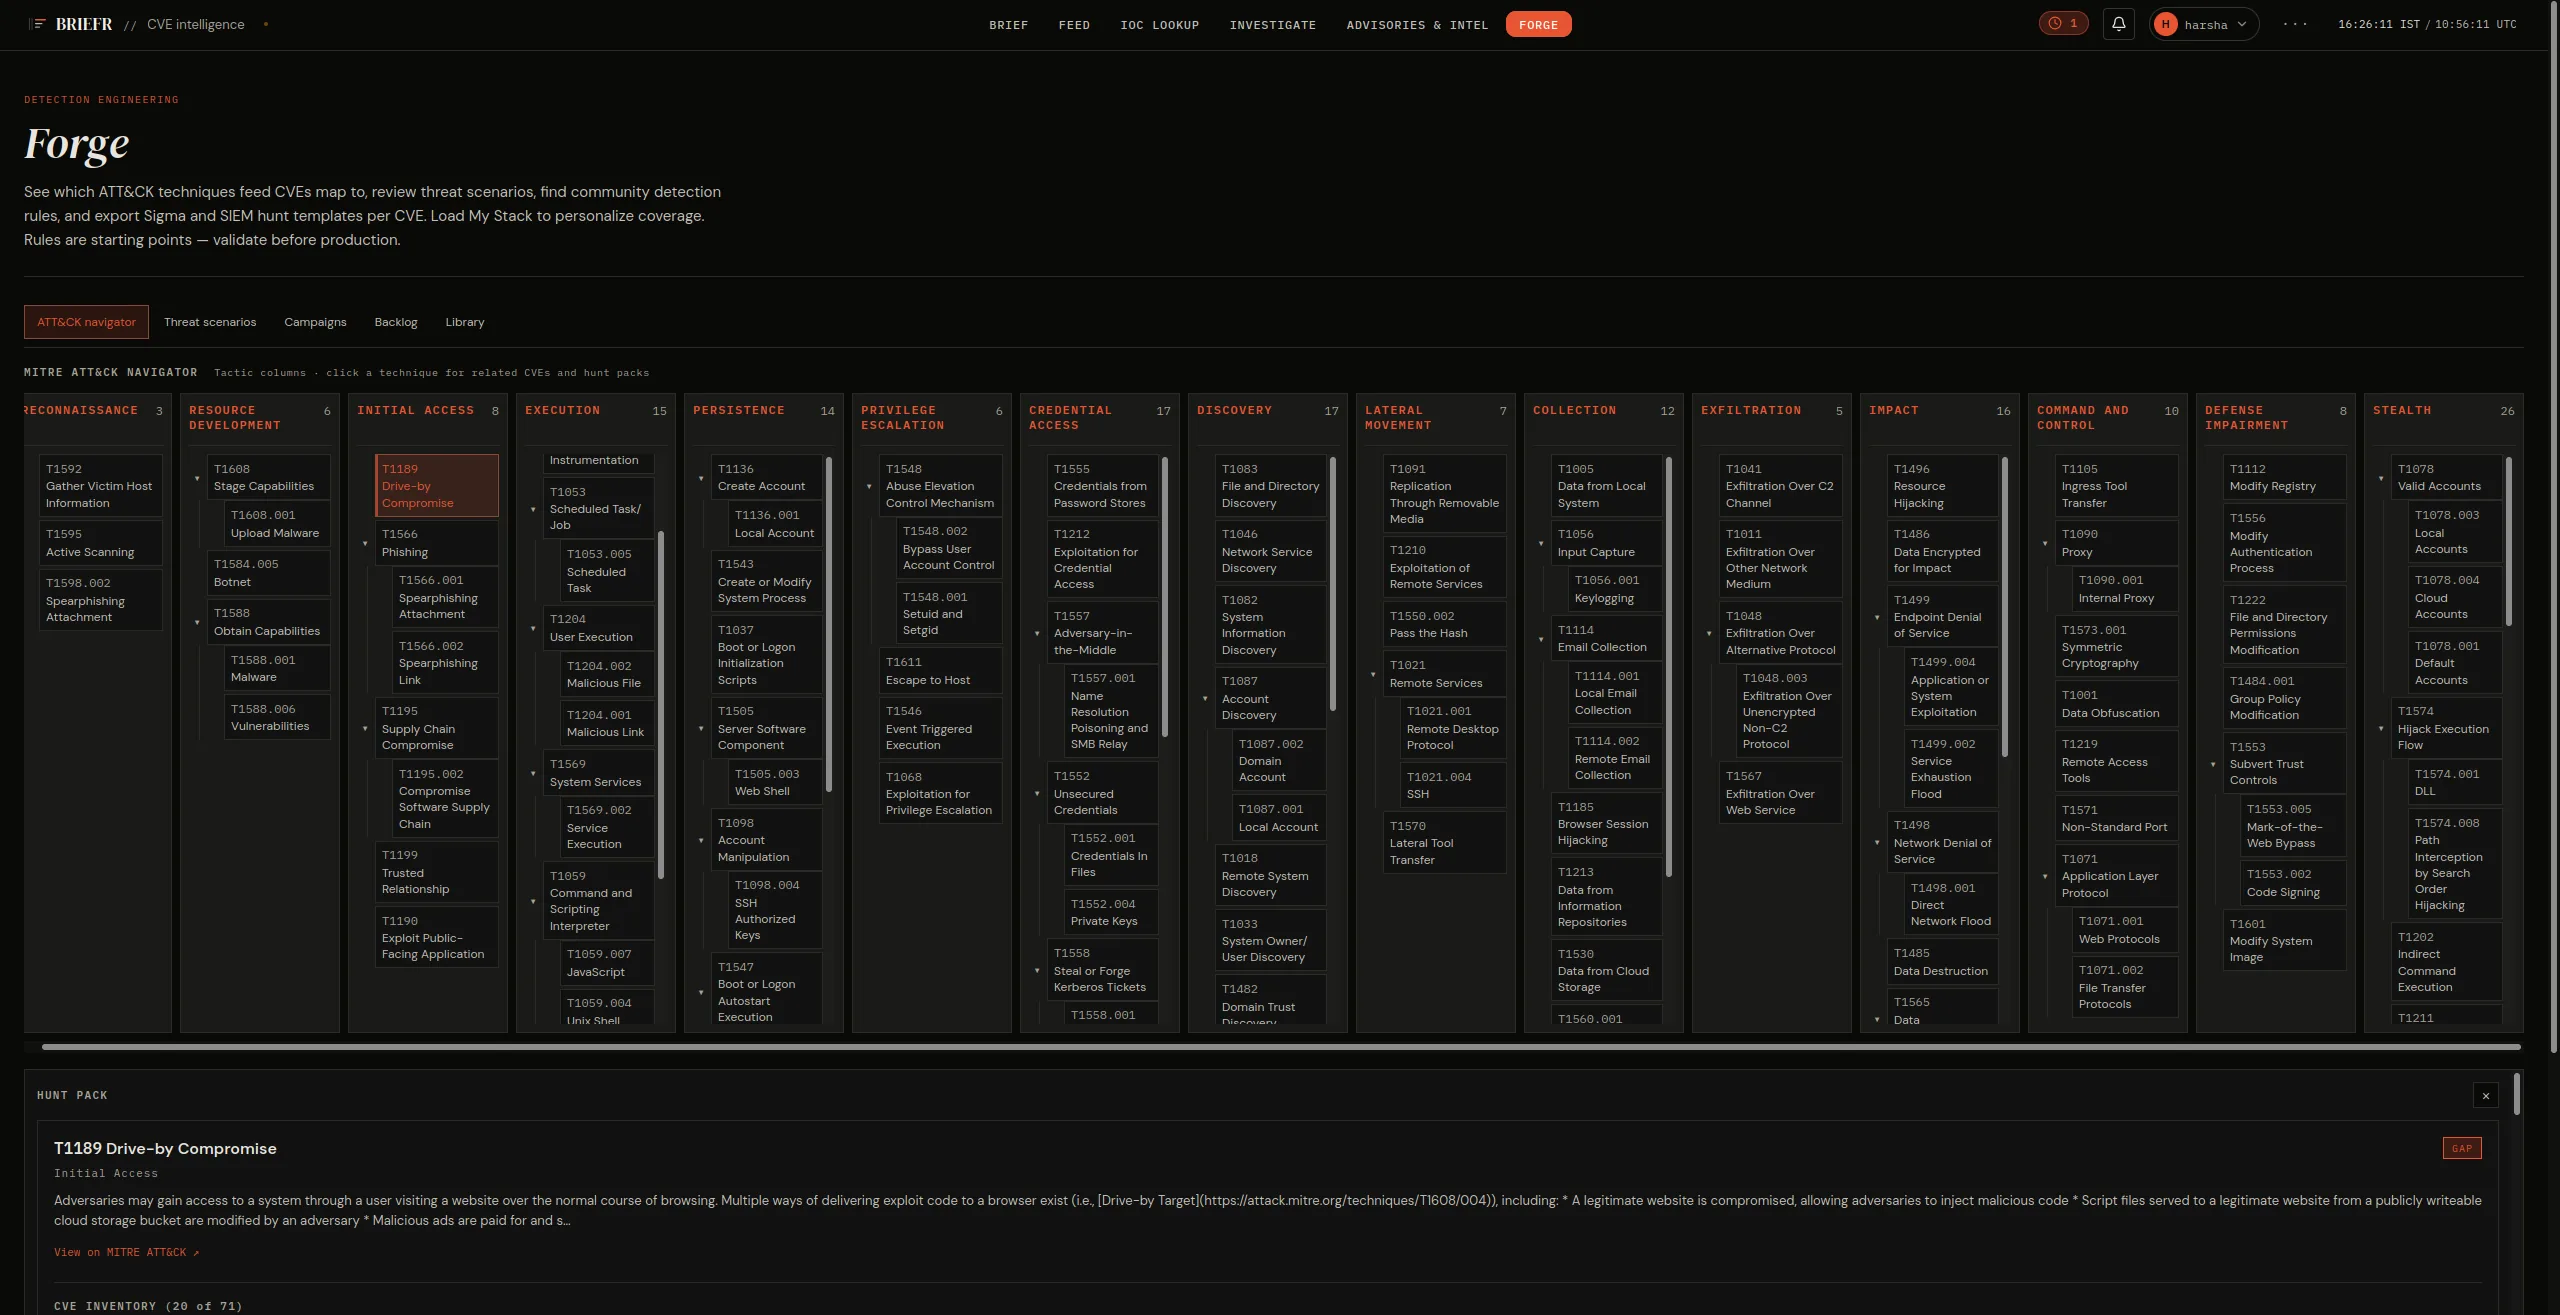
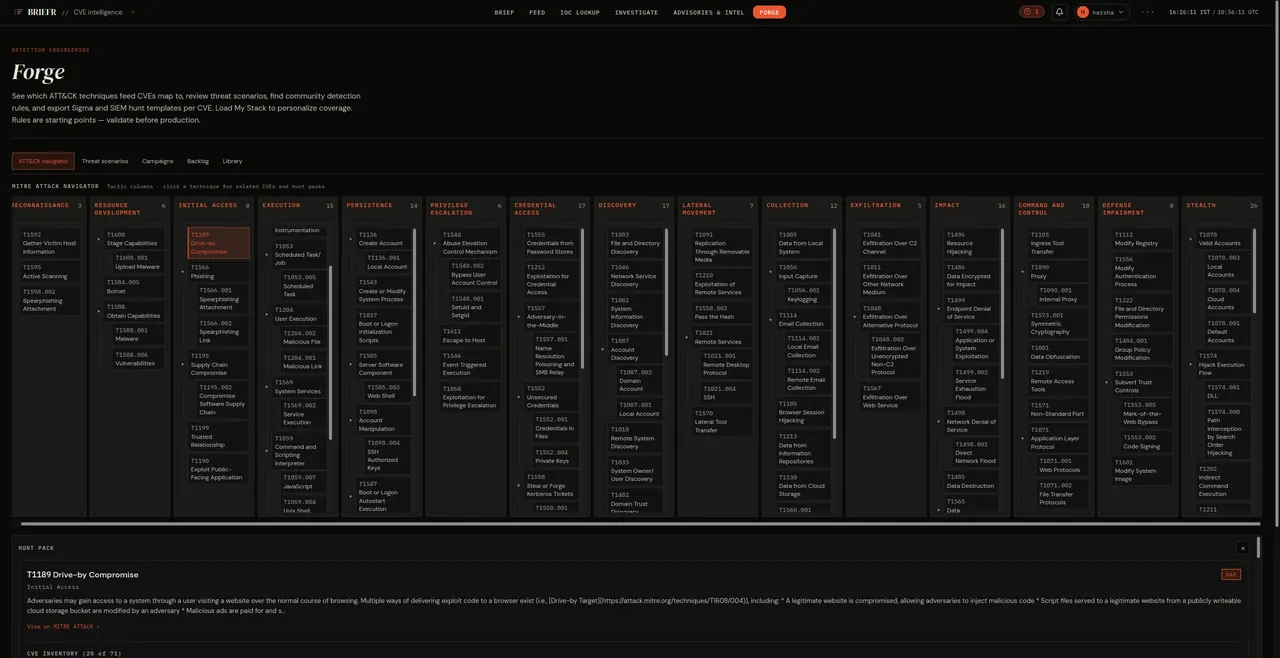
From technique to hunt pack.
See where ATT&CK techniques in your feed have community rules, saved packs, or gaps.
Sigma rules · Elastic, Splunk, Sentinel and QRadar snippets
Screenshot: Briefr Forge MITRE ATT&CK coverage map and hunt pack generation
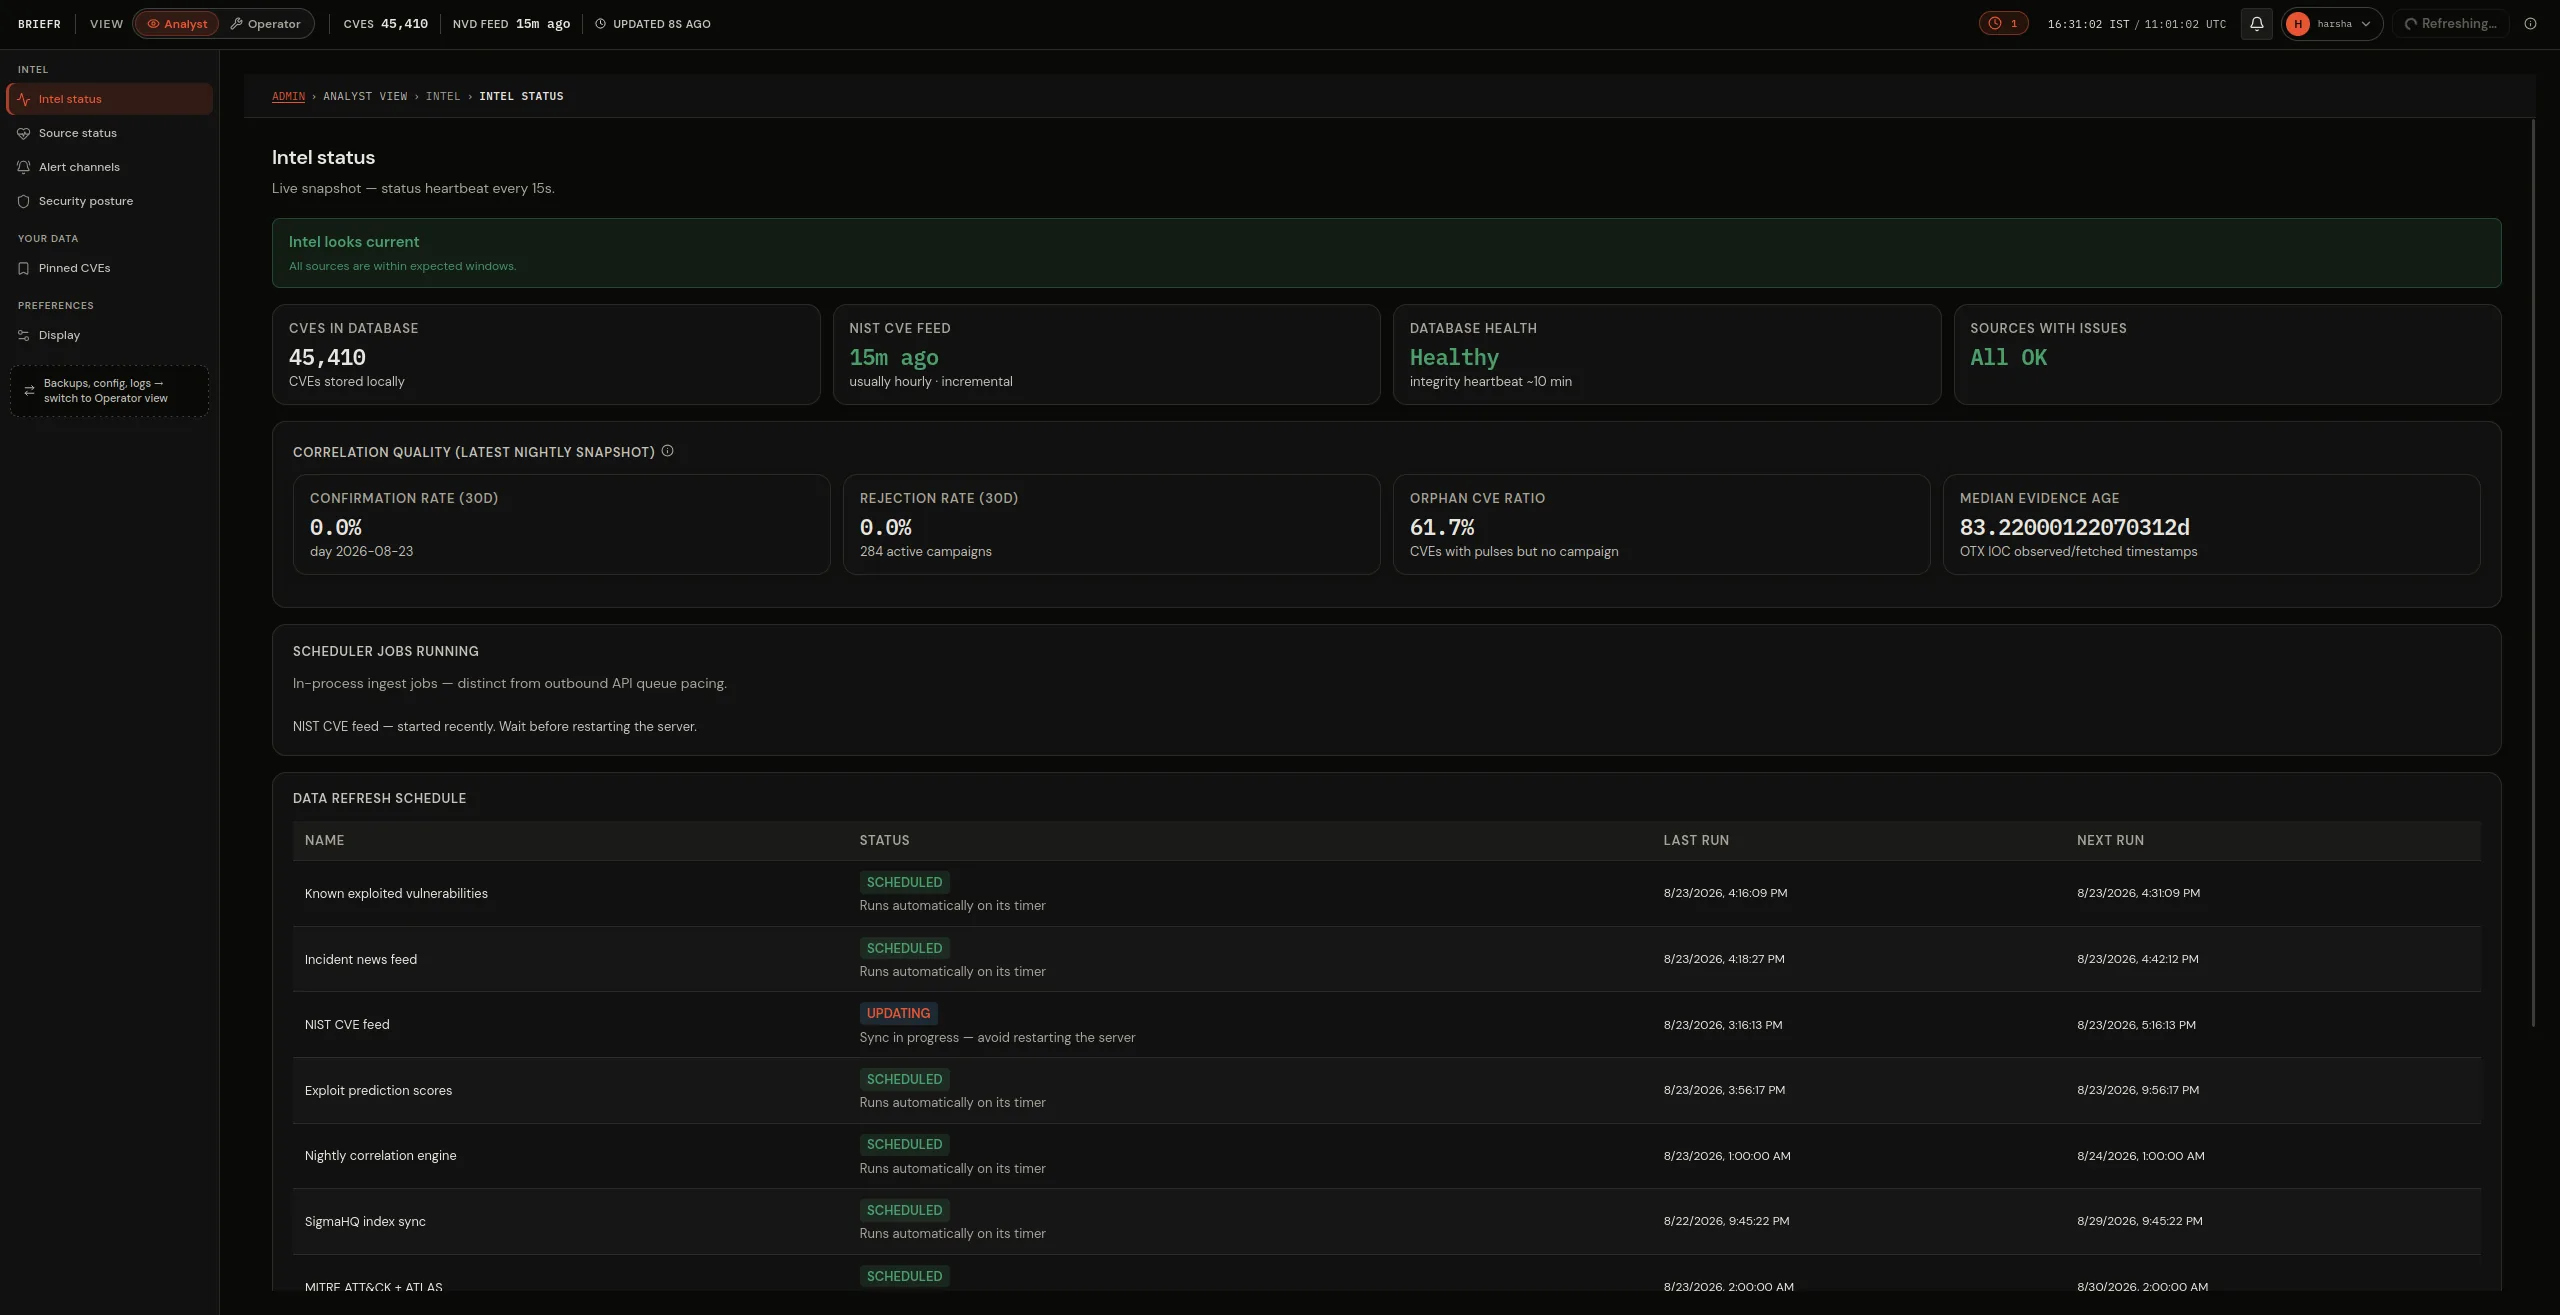
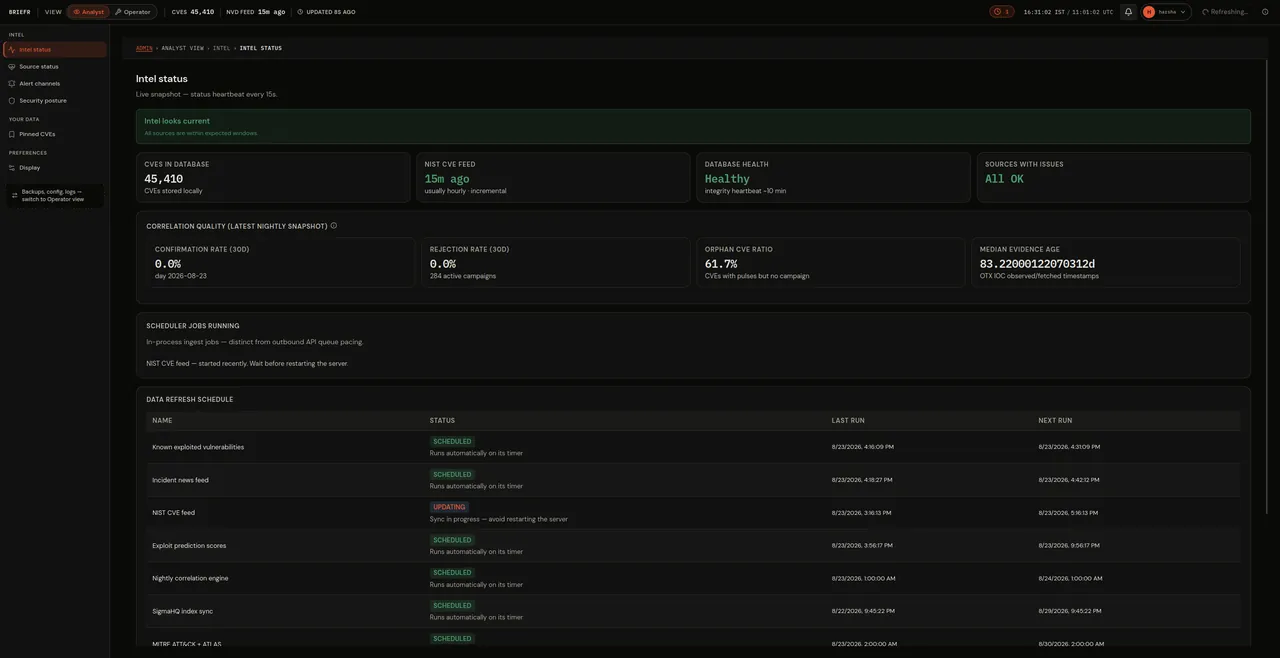
Is the data current? It says so.
Per-source feed health, so you know when to trust the brief and when to wait.
Intel status · source health · alert channels
Screenshot: Briefr admin analyst view with intel status, source health, and alert channels
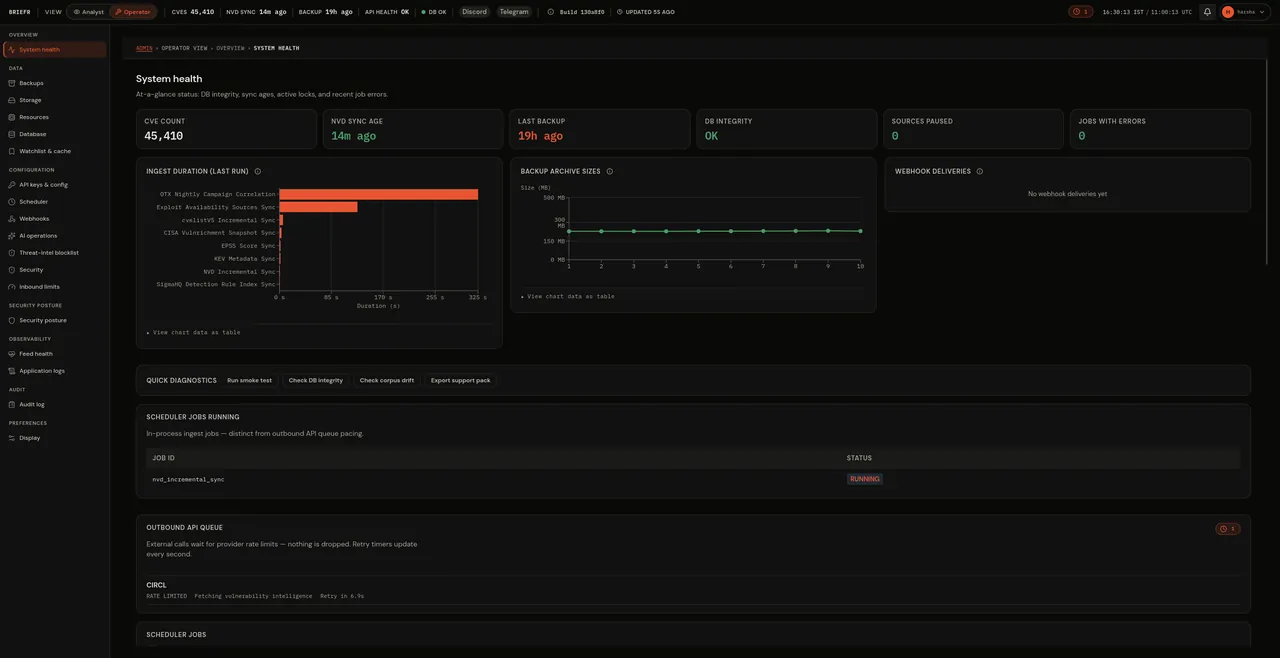
One box you can run yourself.
Scheduler jobs, backups, database integrity and API keys, on hardware you own.
2 cores · 4 GB RAM recommended · 2 GB without the embedding model
Screenshot: Briefr admin operator view with API keys, scheduler jobs, and security posture
A morning in BRIEFR, screen by screen
02 How data reaches you
Nothing is fetched on page load.
03 Scope and limits
Honest by design.
The trade these constraints buy: trust, reproducibility, and a system a small team can actually operate and fully understand.
04 Where it stands
Run it yourself.
BRIEFR is ready to self-host from source today. What is missing is the packaging, not the product.
- Source codeOpen on GitHub under Apache-2.0Ready
- Local deploymentPostgreSQL 16 + pgvector, app built from sourceReady
- Production installdeploy/briefr-install.sh on Debian with nginxReady
- DatabasePostgreSQL 16 + pgvector, compose file includedReady
- Live demoSame analyst shell over fixture dataReady
- Packaged deliveryDocker image and one-command stack are not shipped yetNot yet
Needs Python 3.11+ · Node.js 22.22+ · Git · Docker only for the bundled Postgres
Hardware 2 cores · 4 GB RAM recommended (2 GB without the embedding model)
docker pull pgvector/pgvector:pg16docker run -d --name briefr-postgres -e POSTGRES_USER=briefr -e POSTGRES_PASSWORD=briefr -e POSTGRES_DB=briefr -p 127.0.0.1:5432:5432 pgvector/pgvector:pg16# Those are the defaults. Change the user or password in that command if you need to.# Database URL: postgresql://briefr:briefr@127.0.0.1:5432/briefrgit clone https://github.com/Soldier0x0/briefr.git && cd briefrcd backend && python3 -m venv .venv && source .venv/bin/activatepip install -r requirements-dev.txtcp .env.example .env# Leave .env.example where it is. In backend/.env the fields are already there.# Put your database URL in DATABASE_URL.# Set the other fields to the correct values, including BRIEFR_REQUIRE_POSTGRES, BRIEFR_ENV, and JWT_SECRET.cd ../frontend && npm install && npm run buildcd ../backend && source .venv/bin/activate && uvicorn main:app --host 0.0.0.0 --port 8000# Docker image of BRIEFR# Coming soon05 The larger picture
BRIEFR is the part that shipped.
06 Attribution
Project Jupiter
TLP:CLEARDisclosure is not limited.
Built and maintained by
Sai Harsha Vardhan
Security engineer · threat hunter · platform builder
My background is threat hunting, SIEM operations and data pipelines. I build Project Jupiter so small teams can run analyst-grade intel themselves, and BRIEFR is the first module to ship.
Coverage
- Threat research
- Detection engineering
- Data pipelines
- Backend and API
- Interface and design
- Operations and self-hosting
One maintainer, every layer.
Field experience
- Data Integration Specialist
- Allure Commerce LLPData ingestion and transformation pipelines
- Cyber Threat Hunter
- AtosHunting across SIEM logs and threat intelligence
- Production Support Engineer (L3)
- AtosSIEM middleware application support
- Network & Security Instructor
- Mythri Ojas Training InstituteFoundational cybersecurity
Credentials
- EC-CouncilCEHCertified Ethical Hacker
- EC-CouncilCHFIComputer Hacking Forensic Investigator
- AtosBronzeBronze Accolade, Q1 2024
- Education
- MBA, Information Technology ManagementB.Sc, Computer Science & Electronics
- Provenance
- Every screen in the reel is captured from a running, self-hosted BRIEFR.
- Intelligence sources
- NVD · cvelistV5 · CISA KEV · Vulnrichment · EPSS · MITRE ATT&CK · MITRE ATLAS · OTX · ThreatFox · SigmaHQ · RSS × 5
- Stack
- FastAPI · PostgreSQL 16 + pgvector · React 19
- License
- Apache License 2.0
Contact and disclosure
Found a vulnerability in BRIEFR? Report it privately by email, not in a public issue. The security policy covers coordinated disclosure.